Logging Into KuCoin: Real-World Tips for Spot Trading, Verification, and Staying Sane

Okay, so check this out—logging into KuCoin feels easy until it doesn’t. Really. You click the button, your brain expects a quick trade, and then somethin’ in the flow hiccups: 2FA nagging, verification steps, or an email that never arrives. Hmm… my instinct said it should be seamless, but the exchange world loves to remind you that “seamless” is aspirational.

Here’s the thing. If you’re a US-based trader hopping into spot markets, a quick, reliable kucoin login is mission-critical. Whoa! Missing a price move by five minutes can sting. I’m biased—I’ve lost out on trades because I didn’t sort verification early. Lesson learned the annoying way.

First impressions matter. On one hand, KuCoin’s interface is pretty friendly for spot trading: order books, limit and market orders, familiar charts. On the other hand, account access and identity verification can feel clunky—though actually, wait—KuCoin has improved a lot in the backend over the years. Initially I thought verification was just bureaucratic red tape, but then realized it protects both you and the platform from sketchy behavior.

Screenshot suggestion: KuCoin login screen with 2FA prompt

Quick checklist before you try to log in

Seriously? Yes. Do these quick things and you won’t be juggling recovery codes mid-panic. 1) Use a unique email dedicated to exchanges if you can. 2) Turn on 2FA (prefer authenticator apps over SMS). 3) Prepare a government ID for verification. 4) Save your recovery codes somewhere offline.

One short burst: Wow! Two medium thoughts: If your email inbox is full of promos, that verification link might get buried. So clean it up. One longer note: when you enable 2FA, write down the backup codes and store them physically—on a slip of paper in a safe—because your phone can die, get lost, or be wiped, and then you’re scrambling.

Step-by-step — the typical kucoin login flow

Step 1: Enter email and password. Step 2: Complete 2FA. Step 3: Optional device verification (email link). Step 4: Access spot trading. Pretty linear, though sometimes the platform inserts an extra verification step after suspicious logins, which is frustrating but understandable.

My gut feeling when hitting those extra steps: ugh. But actually, those safeguards catch credential stuffing and account breaches. On one hand you want frictionless access, though on the other hand you want your funds intact. If you travel a lot, expect occasional device checks—so plan ahead and approve logins from known devices when you can.

Verification (KYC) — what they ask and why it matters

KuCoin’s verification levels are about limits and trust. Basic accounts let you browse and trade spot with lower limits, but higher withdrawal caps and some fiat on/off ramps demand identity verification. You’ll upload a government ID, take a selfie, and sometimes answer a few short questions.

Here’s what bugs me about verification: the photo checks can be picky. Tilt your head wrong, and the selfie verification rejects you. I’m not 100% sure why they need that angle, but they do. Pro tip: good lighting, neutral background, and remove hats or glasses. Also, use a modern, valid ID—expired docs are insta-rejects.

Common login problems and how to fix them

Problem: No verification email. Fix: Check spam, promotions, and filters. If still nothing, resend and wait a few minutes—sometimes mail servers lag. Problem: 2FA lost. Fix: Use stored backup codes or contact support with proof of identity (can take time). Problem: Login blocked after suspicious activity. Fix: Follow the device verification steps and, if needed, open a support ticket with timestamps of your last legitimate logins.

A medium aside: support waits can frustrate you. (oh, and by the way…) Keep screenshots and transaction IDs handy when you open a ticket—this speeds things up. One long thought: sometimes the “fix” requires patience—bank transfers and identity checks don’t follow crypto market time; they follow compliance time, which is slower and more annoyingly human.

Spot trading specifics after you get in

Spot trading on KuCoin is straightforward: pick a pair, set order type, execute. But watch out for liquidity on smaller pairs; slippage can bite. My instinct said I could scalp a thin altcoin quickly, until order books moved and I was left holding tokens that dumped—again, lesson learned.

Use limit orders when you can. Use stop-limit for protection, not market panic orders unless you accept slippage. Check fee tiers—higher KCS holdings can reduce fees, and reducing fees matters for frequent traders. Also, enable price alerts rather than refreshing the app obsessively; your heart will thank you.

Security best practices

Two short tips: Never reuse passwords. Never. Medium explanation: Use a reputable password manager, enable 2FA via Authenticator apps (Google Authenticator, Authy), and remove SMS-based 2FA when possible. Long thought: Consider whitelisting withdrawal addresses for significant wallets—this adds a layer where even if credentials are compromised, withdrawals need pre-approved addresses, which dramatically reduces theft risk.

I’m biased: on-chain custody of large holdings feels safer if you control your private keys. But for active spot trading you need exchange liquidity. So the balanced approach is clear: keep trading capital on the exchange and store the rest in hardware wallets. On one hand it’s a pain, though on the other hand, you sleep better.

FAQ — quick answers to common questions

Why didn’t my verification go through?

Usually it’s the photo quality or mismatched details. Make sure your ID matches your account name exactly, use good light for selfies, and avoid filters or heavy editing. If rejections persist, contact support and include clear photos and timestamps.

Can I trade without KYC?

To an extent, yes—basic spot trading is possible with limited withdrawals. But larger withdrawals, fiat channels, and some features require verification. If you plan to move significant funds, do KYC early to avoid delays.

What if I lose my 2FA device?

Use your saved backup codes to regain access. If you don’t have them, you’ll need to submit a support request with identity proof. That can take days, so store backup codes offline right away.

Alright—circling back. You started this wanting to log in fast and maybe catch a trade. Now you know the steps, the common traps, and the pragmatic balance between convenience and security. Something felt off about diving in without prepping, and my instinct was right: setup and verification take a few minutes now but save hours (and money) later.

I’ll leave you with this: tidy your inbox, secure your 2FA, and don’t keep everything on the exchange. I’m not perfect—I’ve messed up two times—but those mistakes taught me more than any how-to ever could. Trade smart, and when you need the link, here’s the straightforward place to start your session: kucoin login.

Rabby Wallet en Polygon, Arbitrum y Optimism: Guía de redes soportadas

Un usuario de Ethereum que maneja posiciones en Polygon, Arbitrum y Optimism enfrenta un problema operativo: cada red requiere su propia gestión de activos, conexiones y configuraciones. Cambiar entre ellas en billeteras tradicionales implica procesos manuales, riesgo de errores de red y una experiencia fragmentada. Rabby Wallet resuelve esta fricción mediante soporte nativo para más de 100 blockchains EVM, permitiendo que un usuario interactúe con todas sus posiciones desde una única interfaz sin perder control sobre sus claves privadas.

La arquitectura no custodial de Rabby significa que las claves permanecen cifradas en el dispositivo del usuario, no en servidores remotos. Esto es particularmente relevante al operar en múltiples cadenas, donde la exposición a plataformas de custodia aumenta el riesgo. La billetera detecta automáticamente la red correcta según el contrato inteligente con el que el usuario intenta interactuar, elimina pasos de configuración manual y presenta una vista unificada del portfolio que consolida tokens y NFTs de todas las redes soportadas en un solo lugar.

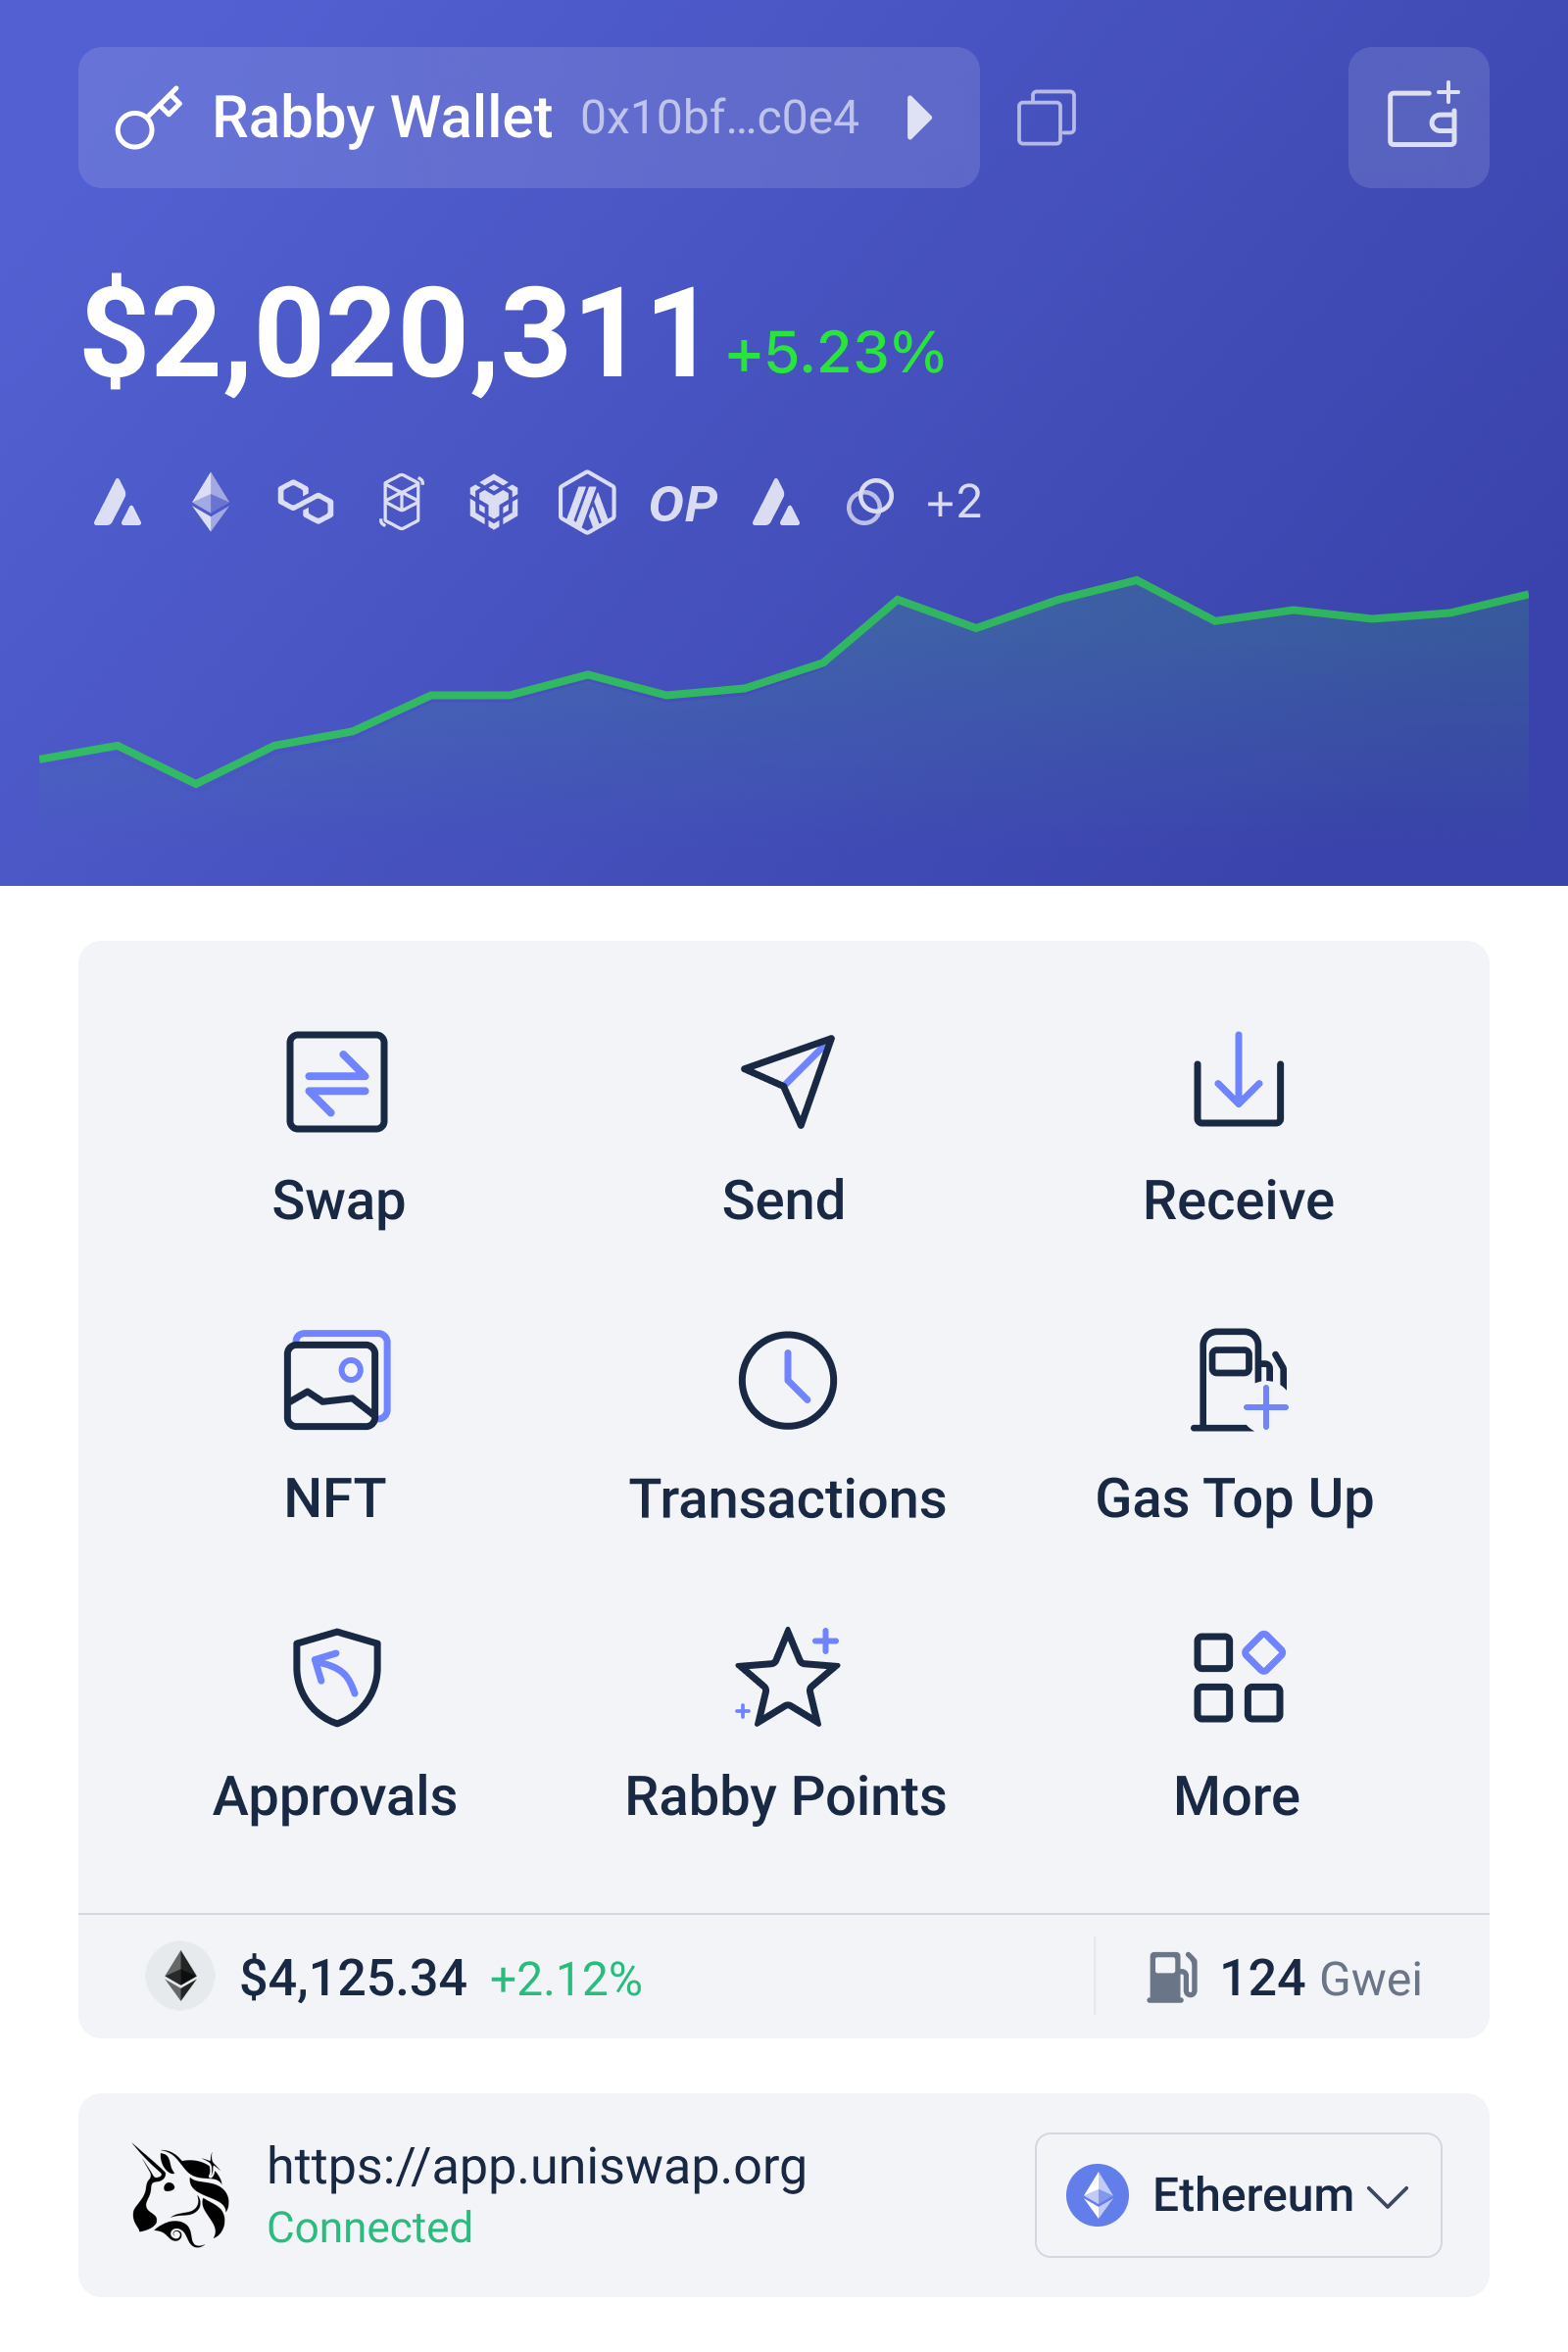
Interfaz de Rabby Wallet mostrando la gestión de múltiples cadenas EVM con vista consolidada de activos y portfolio

Polygon: escalado de Ethereum con costos accesibles

Polygon (anteriormente Matic) es una cadena EVM que procesa transacciones en paralelo a Ethereum, manteniendo compatibilidad con su ecosistema de herramientas y contratos. Los costos de transacción en Polygon son significativamente más bajos que en Ethereum mainnet, típicamente en el rango de centavos en lugar de dólares, lo que permite estrategias de trading más frecuentes, provisioning de liquidez en AMMs y transferencias de activos sin fricción. Para un usuario que gestiona posiciones en lending protocols, yield farms o mercados NFT, esta diferencia de costo transforma operaciones que serían antieconómicas en Ethereum en flujos de trabajo prácticos.

Rabby reconoce automáticamente cuando un usuario intenta conectarse a una dApp de Polygon, ajustando la configuración de red sin intervención manual. Esto es especialmente importante porque los usuarios a menudo cometen errores al cambiar redes manualmente en billeteras competidoras: un clic mal dirigido puede enviar fondos a la dirección incorrecta en la cadena equivocada, resultando en pérdida permanente. La simulación de transacciones de Rabby también actúa como un control previo a la firma, mostrando exactamente qué cantidad de tokens saldrá del wallet, qué recibirá el usuario, y si hay riesgos evidentes como intentos de aprobación sin límite o interacciones con contratos nuevos.

Para usuarios de Polygon, una gestión estratégica de liquidez incluye seguimiento de posiciones en Aave, Curve, Balancer y otros protocolos DeFi. La vista unificada de Rabby consolida estos saldos de forma que un usuario puede ver inmediatamente si tiene suficiente MATIC para pagar comisiones, cuánto USDC está depositado en lending y qué NFTs mantiene en colecciones. Esta visibilidad reduce el riesgo de aprobar transacciones basadas en información incompleta, que es cómo ocurren muchos errores en operaciones multi-cadena.

Arbitrum: velocidad y liquidez concentrada

Arbitrum es un rollup optimista que procesa cálculos fuera de la cadena y publica pruebas de validez en Ethereum, logrando una combinidad de seguridad heredada y velocidad de confirmación. Las transacciones se finalizan mucho más rápido que en Ethereum mainnet, y los costos siguen siendo una fracción de los costos de Ethereum, aunque típicamente superiores a Polygon. Para trading de alta frecuencia, operaciones de arbitraje y estrategias que requieren múltiples transacciones interconectadas, Arbitrum ofrece un balance pragmático entre economía y confirmación rápida.

El ecosistema de Arbitrum incluye exchanges descentralizados como GMX, Camelot y Uniswap V3, donde la liquidez es lo suficientemente profunda para soportar posiciones significativas. Un usuario con exposición en varios pares de trading necesita entender el estado de sus órdenes, márgenes disponibles, y tasas de financiación en tiempo real. Rabby facilita esto consolidando datos de múltiples protocolos sin requerir que el usuario abra diez pestañas. La gestión avanzada de aprobaciones es particularmente relevante en Arbitrum porque estos protocolos a menudo solicitan aprobaciones de monto ilimitado, aumentando el riesgo de exploit si el contrato es comprometido. Rabby permite al usuario revisar exactamente cuánto está aprobando antes de firmar.

Un detalle técnico importante: Arbitrum emplea un mecanismo de rebase de gas donde los costos incluyen una componente de L1 (envío a Ethereum) y una componente de L2 (cálculo en Arbitrum). Rabby estima estos costos de forma combinada, mostrando el costo total que el usuario pagará, no solo el componente L2. Esto es crucial para evitar sorpresas al presupuestar operaciones.

Optimism: EVM equivalencia y tokens nativos

Optimism es otro rollup optimista que prioriza la equivalencia con la máquina virtual Ethereum (EVM), lo que significa que los contratos inteligentes se comportan de forma casi idéntica a como lo harían en Ethereum mainnet. Esta compatibilidad reduce la fricción para desarrolladores migrando aplicaciones, lo que resultó en un ecosistema robusto de protocolos DeFi, DEXs y mercados de tokens. Desde la perspectiva del usuario, Optimism se siente más similar a Ethereum que Polygon o Arbitrum, porque la mayoría de los patrones de interacción son directamente transferibles.

El token OP proporciona gobernanza descentralizada, y muchos protocolos en Optimism distribuyen incentivos adicionales para usuarios tempranos. Un usuario que participa en lending en Aave Optimism, provisioning de liquidez en Velodrome (un AMM optimizado para Optimism), o staking en protocolos incentivados necesita consolidar estos rendimientos e identificar qué activos son más valiosos para reinvertir. Rabby proporciona esto de forma automática mediante la vista unificada de portfolio, que calcula el valor total en USD (o en la moneda de preferencia del usuario) a través de todas las posiciones y redes.

Optimism también implementa un mecanismo de secuenciador centralizado que ordena transacciones, lo que reduce la latencia comparado con Arbitrum pero introduce un punto de centralización. Para transacciones simples (transferencias, aprobaciones), esto no es una consideración práctica. Para operaciones sensibles al timing como flashloans o arbitraje, entender este factor es valioso. Rabby no oculta estas distinciones; su interfaz respeta los tiempos de bloque de cada cadena.

Cambio automático de red y configuración sin fricción

La característica de cambio automático de red en Rabby opera de la siguiente manera: cuando un usuario navega a una dApp ejecutada en Arbitrum, Rabby detecta la URL y la configuración de red requerida, luego solicita al usuario cambiar su billetera a esa red con un único clic. Esto elimina una fuente común de error en la que usuarios confunden qué red está activa, resultando en transacciones fallidas o envíos a direcciones incorrectas. El sistema también funciona a la inversa: si un usuario intenta interactuar con un contrato que no existe en la red activa, Rabby alerta en lugar de permitir que la transacción fracase silenciosamente.

La configuración de una billetera nueva en Rabby requiere crear o importar una semilla de recuperación (seed phrase), que Rabby cifra inmediatamente en el dispositivo usando un estándar de cifrado robusto. Esto ocurre una sola vez durante la instalación. Las claves privadas nunca se transmiten a servidores de Rabby; la compañía nunca conoce las semillas de los usuarios. Este diseño contrasta con billeteras custodiales donde el proveedor mantiene las claves en servidores. Aunque Rabby es más seguro en este aspecto, el usuario sigue siendo responsable de proteger su dispositivo y su frase de recuperación contra malware y acceso físico no autorizado.

Para usuarios con múltiples dispositivos, Rabby permite sincronización de preferencias a través de una función de sincronización opcional, pero las claves privadas nunca se sincronizan automáticamente. Si el usuario decide sincronizar entre dispositivos, la semilla debe ser importada manualmente en cada uno. Esta fricción adicional es intencional: garantiza que el usuario mantiene control explícito sobre dónde existen sus claves.

Compatibilidad con hardware wallets y seguridad de claves

Rabby se integra con hardware wallets como Ledger, Trezor y Keystone, permitiendo que usuarios mantengan sus claves privadas en un dispositivo desconectado mientras interactúan con dApps a través de Rabby. Este enfoque separa la toma de decisiones (qué transacción aprobar) del almacenamiento de secretos (las claves reales), proporcionando defensa contra malware en la computadora principal que intenta robar claves. Cuando un usuario conecta un hardware wallet a Rabby, la billetera puede generar transacciones y mostrarlas en el hardware wallet para revisión y firma; la clave privada nunca abandona el dispositivo.

Para usuarios con carteras significativas en Polygon, Arbitrum y Optimism, la integración de hardware wallet es una consideración seria. Una exposición acumulativa de decenas de miles de dólares en múltiples cadenas justifica el costo y la fricción operacional de un hardware wallet. El flujo de trabajo es: conectar el hardware wallet a Rabby vía USB, seleccionar la dirección derivada que se desea usar (la mayoría de hardware wallets soportan múltiples direcciones desde una sola semilla), luego proceder normalmente. Cuando se necesita firmar, Rabby le pide al usuario que confirme en el dispositivo físico.

La aplicación desktop nativa de Rabby para Windows, macOS y Linux proporciona otra capa de seguridad comparado con extensiones de navegador, que tienen acceso más amplio a los datos del navegador. Un usuario preocupado por la seguridad podría usar la aplicación desktop con un hardware wallet para las operaciones más sensibles, y la extensión de navegador para verificaciones de saldos e investigación. Puede descargar aquí la versión que se adapte mejor a su flujo de trabajo.

Simulación de transacciones y prevención de errores costosos

La simulación de transacciones es una característica que ejecuta una transacción de forma local antes de enviarla a la cadena, mostrando exactamente qué ocurrirá si se aprueba. Cuando un usuario interactúa con un protocolo DeFi complejo, especialmente uno con múltiples pasos (por ejemplo, aprobar token A, canjear por token B mediante un contrato inteligente, luego depositar token B en un protocol de lending), la simulación reduce la incertidumbre. Si hay un error en la lógica del contrato, revertería durante la simulación, alertando al usuario antes de que envíe la transacción real y gaste comisiones.

En Polygon, donde las comisiones son bajas, los errores son menos costosos; un usuario puede permitirse experimentar más. En Arbitrum y Optimism, donde las comisiones aún son significativas para operaciones complejas, la simulación ahorra dinero de forma consistente. Un patrón común es que usuarios intentan interactuar con contratos recientemente desplegados cuya lógica contiene bugs. Sin simulación, la transacción falla después de consumir gas, resultando en pérdida de comisiones sin cambio en el estado. Con simulación, el usuario ve el fracaso de antemano.

Rabby también advierte cuando un usuario intenta aprobar un contrato para acceder a una cantidad ilimitada de tokens, una práctica que amplifica el riesgo si el contrato es comprometido. Por ejemplo, si un usuario aprueba una cantidad ilimitada a un DEX falso, ese contrato podría drenar todos los tokens aprobados. Rabby no bloquea estas aprobaciones (el usuario mantiene control), pero sí pregunta “¿realmente quieres aprobación ilimitada?” Un usuario informado generalmente especifica una cantidad máxima igual al monto que planea usar en esa transacción única.

Vista unificada de portfolio y gestión de NFTs

Una de las ventajas menos obvias de Rabby es que consolida tokens y NFTs de todas las redes soportadas en un solo dashboard. Un usuario con USDC en Polygon, ETH en Arbitrum, OP en Optimism y un NFT en cada cadena normalmente necesitaría visitar cinco interfaces diferentes para obtener una imagen completa. Rabby calcula automáticamente el valor total, muestra la composición de activos, e identifica cuál de esos activos está actualmente en riesgo (por ejemplo, si se utilizan como colateral en un protocolo de lending y están llegando cerca de un precio de liquidación).

El seguimiento de NFTs es particularmente valioso porque los mercados de NFT están fragmentados por cadena y plataforma. Un usuario con colecciones en OpenSea (Ethereum), Arbitrum, Polygon y Optimism puede perder el seguimiento de dónde están exactamente sus activos si no tiene una vista consolidada. Rabby lista todos los NFTs, mostrando la cadena, el contrato, el ID del token y el valor estimado. Esto facilita tomar decisiones informadas sobre cuál vender, qué es valorable para mantener a largo plazo, y qué puede ser enviado a otra cadena si es necesario.

La volatilidad de precios en diferentes cadenas es un factor real en estrategias sofisticadas. Un token puede valer más en una cadena que en otra debido a diferencias en liquidez de mercado, aranceles de bridge y demanda local. Rabby no realiza arbitraje automáticamente, pero proporciona la información que un usuario sofisticado necesita para identificar oportunidades y ejecutarlas manualmente o mediante un script externo.

Instalación y acceso multi-plataforma

Rabby está disponible como extensión de navegador para Chrome, Brave, Edge y Firefox, lo que significa que la mayoría de usuarios pueden instalar sin buscar ningún software especial. La extensión se integra en la barra de herramientas del navegador y aparece cuando es necesaria, sin ralentizar el navegador significativamente. Para usuarios de navegadores menos comunes o preocupados por la privacidad del navegador, la aplicación desktop nativa para Windows, macOS y Linux proporciona la misma funcionalidad sin depender de la extensión. La app móvil para Android en Google Play (con más de 100,000 descargas) permite realizar transacciones y verificar saldos desde un teléfono, aunque la mayoría de usuarios mantienen montos menores en el móvil que en sus dispositivos principales.

iOS está en desarrollo, lo que significa que usuarios de iPhone actualmente no tienen una opción nativa oficial. Este retraso es típico en el desarrollo de Web3 debido a restricciones de la App Store de Apple sobre carteras autocustodiadas, aunque algunos proveedores han navegado estos requisitos con arquitecturas intermedias. Para usuarios de iPhone, Rabby sigue siendo accesible a través del navegador Safari si deciden usar la versión web, aunque esta no proporciona el mismo nivel de integración que una app nativa.

La instalación inicial es directa: descargar desde el navegador o tienda de aplicaciones, crear una nueva billetera (o importar una semilla existente), establecer una contraseña local, y confirmar la frase de recuperación escribiéndola offline. El proceso toma alrededor de cinco minutos. Después, el usuario puede comenzar inmediatamente a interactuar con dApps en Polygon, Arbitrum, Optimism y otras cadenas soportadas.

Preguntas frecuentes

¿Necesito crear billeteras separadas para Polygon, Arbitrum y Optimism?

No. Una sola semilla de recuperación en Rabby genera múltiples direcciones, una para cada cadena (técnicamente, la misma dirección funciona en todas las EVM due a su compatibilidad, pero la actividad y los saldos se rastren separadamente). Rabby cambia automáticamente entre redes según la dApp con la que interactúes, sin requerir múltiples billeteras.

¿Qué sucede si envío tokens de Polygon a una dirección de Ethereum?

Si envías MATIC de Polygon a una dirección de Ethereum mainnet sin usar un bridge, los fondos se enviarán a esa dirección en Polygon, no en Ethereum, y serán inaccesibles desde Ethereum (aunque tecnicamente la dirección sigue siendo válida en ambas redes, los MATIC quedan en Polygon). Siempre verifica que la red receptora sea correcta antes de confirmar. Rabby alerta cuando detecta una red incorrecta, pero no puede prevenir cada posible error.

¿Es seguro usar Rabby con cantidades grandes de fondos?

Rabby es no custodial, por lo que tus claves permanecen bajo tu control, no en servidores de Rabby. Para cantidades significativas, la integración con un hardware wallet (Ledger, Trezor o Keystone) proporciona protección adicional contra malware. La seguridad final depende de cómo protejas tu dispositivo y tu frase de recuperación. Rabby proporciona las herramientas; el usuario implementa las prácticas.

When Your Swap Fails or Gets Front-Run: How Transaction Simulation, MEV Protection, and dApp Integration Change the Game

You’re about to send a multi-step DeFi transaction: swap ETH for USDC, then supply liquidity, then stake the LP token. You check gas, hit submit, and — two blocks later — the frontend shows a partial fill, higher slippage, or worse, the transaction reverted and you lost the gas. This simple scenario captures three hard truths of modern Ethereum and EVM chains: transactions are not atomic in the face of mempool manipulation and on-chain state updates; miners/validators and bots can reorder or sandwich transactions for profit; and the UX surface (wallet + dApp) often lacks the instruments to preview, prevent, or repair these outcomes.

In practice, two technical tools — robust transaction simulation and MEV (miner-extractable value) protection — plus thoughtful dApp integration, change the user’s leverage dramatically. This article explains how these mechanisms work, what they cannot guarantee, and how a DeFi user should weigh trade-offs when choosing a wallet or connecting to a dApp. I’ll highlight operational limits and offer a compact decision framework you can reuse when evaluating wallets and integrations.

Illustration of a wallet UI showing transaction preview, simulated state changes, and MEV protection options

What transaction simulation actually does (and what it doesn’t)

At its core, transaction simulation executes your intended transaction against a recent state snapshot without broadcasting it to the public mempool. Mechanically, the wallet or provider forms the signed transaction and runs it on a node or a local EVM fork to see the outcome: success or revert, gas used, token amounts, and any internal calls. A correct simulation reveals immediate failure modes (insufficient funds, revert reasons) and surface outcomes (slippage, partial fills) under the simulated state.

Important boundary conditions: simulation is only as accurate as the state and assumptions it uses. If the simulation runs against a node that lags the chain, or if other pending transactions in the mempool will change contract state before your transaction, the simulation’s prediction can be wrong. Similarly, gas price changes and front-running strategies can alter execution order; simulation cannot perfectly predict ordering in a competitive mempool without modeling adversarial actors.

Why this matters: a good wallet that provides simulation reduces false positives (failed transactions you didn’t expect) and false negatives (transactions that look fine but will fail). Simulation makes the invisible visible — allowing the user to see likely token outputs, estimated gas consumption, and revert traces. The mental model shifts from “I hope the swap goes through” to “I can inspect and adjust parameters before risking on-chain gas.”

MEV protection: mechanism, trade-offs, and realistic limits

MEV refers to the extra value available to the party that controls transaction ordering (miners, validators, or sequencers). Protection strategies aim to remove or reduce the ability of third parties to reorder, insert, or sandwich transactions. Common approaches include private transaction relays, bundle submissions to validators, pre-signed transactions with Guaranteed Ordering (for certain sequencers), or on-chain mechanisms like limit orders and atomic matchers.

Mechanism clarity is crucial. Private relays send your transaction off-mempool to a set of validators or builders, preventing general bots from seeing it. Bundles allow you to package several instructions so they execute atomically or in a defined sequence. But these systems impose trust or availability trade-offs: private relays may be operated by centralized services with uptime and censorship policies you must accept; bundles depend on honest builder behavior and timely inclusion by a validator; and using these services often increases latency or incurs extra fees.

Limits worth stating plainly: MEV protection reduces some classes of extraction but cannot eliminate all risk. Sophisticated attackers may still detect patterns, exploit cross-chain state, or use out-of-band coordination. Network-level features like proposer-builder separation (PBS) improve the ordering market but do not abolish incentives. For a US-based DeFi user, the correct attitude is risk-aware: use MEV protection where the expected value at stake (lost slippage, sandwich costs, or front-run risk) exceeds the combined cost and trust premium imposed by the protection method.

How wallets and dApps should integrate simulation and MEV features

Integration matters. A wallet can simulate a transaction but if the dApp doesn’t expose the underlying parameters (e.g., the slippage tolerance or the intermediate route), the simulation is less useful. Best practice is a two-way contract: the dApp presents a precise intent (router call, path, deadlines), the wallet simulates against that exact call, and the wallet offers an action — approve, alter parameters, or submit via a private relay/bundle — with clear trade-offs.

From a UX and security perspective, watch for four capabilities: atomic multi-step simulation (simulate the entire pipeline rather than each call separately), readable revert traces (so you can see which sub-call would fail), MEV submission options with explicit cost/benefit display, and deterministic nonce and gas strategies so that retries are predictable. A wallet that surfaces these features reduces cognitive load and improves decision-making.

One practical integration pattern: the dApp exposes an unsigned bundle that describes the user’s intent. The wallet simulates the bundle, shows expected outcomes, and can submit the bundle to a private relay or a validator through a relay API. That pattern keeps visibility limited while preserving the user’s ability to validate the exact sequence that will run on-chain.

Common myths vs reality

Myth: “Simulation guarantees my transaction will succeed.” Reality: simulation is predictive, not prophetic. It can show whether the transaction would succeed on the simulated state, but cannot predict other actors’ future transactions or mempool ordering. Treat simulation as high-quality conditional information: “If the world stays like this, this is what happens.”

Myth: “MEV protection is either free or pointless.” Reality: effective MEV mitigation has costs (fees, latency, trust trade-offs) and benefits (reduced slippage and lower sandwich risk). The return on paying for protection is proportional to the expected extractable value your transaction presents; small retail trades may not justify the cost, whereas large rebalances or arbitrage-sensitive operations might.

Myth: “All wallets offer the same protection and integration.” Reality: implementations differ widely. Some wallets only show a basic simulation (gas + success/revert), others provide deep execution traces, bundle submission, and configurable MEV options. Evaluate the exact features rather than relying on marketing language.

Decision framework: when to simulate, when to use MEV protection, and how much trust to accept

Here is a compact heuristic to apply before sending a transaction:

– Step 1: Simulate locally. Always run a simulation on the exact call the dApp will send. If the simulation shows a revert or unexpected token amounts, stop and investigate parameters.

– Step 2: Quantify stake and sensitivity. Estimate how much you’d lose if your transaction were sandwiched or front-run. Compare that expected loss to the fees and trust cost of MEV protection.

– Step 3: Choose submission path. For low-sensitivity trades, use normal mempool submission but keep slippage tight and deadlines conservative. For medium-to-high sensitivity, prefer bundle submission or a private relay that explicitly publishes inclusion guarantees and fee schedules.

– Step 4: Validate post-submission. Check inclusion traces and receipts. If the wallet supports post-facto analysis (detecting suspicious reorderings or unexpected intermediate states), use it to adjust future behavior.

Operational limitations and unresolved questions

Two unresolved tensions are worth noting. First, decentralization vs. practicality: many MEV-mitigation approaches push traffic through centralized relays or builders, reintroducing single points of failure and censorship risk. Second, modeling adversarial behavior remains an open systems problem — simulations that incorporate realistic adversary models (probable front-running bots, cross-DEX arbitrageurs) are early-stage and computationally costly.

These limitations imply practical trade-offs: you can reduce visible risk at the cost of adding trust and possibly higher fees. A wallet or dApp promising “complete protection” is overpromising; intelligent products make the trade-offs explicit and let users choose based on stakes and tolerance.

What to watch next — conditional signals that matter

Keep an eye on three signals that will shape the next year of wallet and dApp behavior: wider adoption of proposer-builder separation and open builder markets (which alter ordering dynamics); the maturity of private relay networks and their transparency policies; and practical UX innovations that make simulation, bundle construction, and MEV choices intelligible to ordinary users. If relays standardize APIs and give public audit logs, trust costs fall and MEV protection becomes cheaper and more reliable for typical users.

In the US regulatory context, also watch for policy attention on transaction ordering and potential disclosure or operational constraints — changes that could shift where and how wallets route transactions.

For DeFi users deciding which wallet to trust for advanced simulation and MEV protection, inspect three concrete features: the fidelity of simulation (does it simulate the exact RPC and the full call graph?), available MEV submission paths (relay, bundle, sequencer), and transparency about trade-offs and fees. If you want a starting point that emphasizes on-chain clarity and EVM coverage, consider a wallet that foregrounds simulation and security built into its UX, and experiment with small, incremental usage before committing larger stakes; for example, explore how rabby wallet surfaces simulation and chain coverage across EVM networks.

FAQ

Q: Can simulation stop all failed transactions?

A: No. Simulation reduces the chance of surprising reverts by revealing problems that exist in a specific blockchain state snapshot. It cannot predict transactions from other users or bots that will change state or how validators will order mempool transactions. Think of simulation as a high-quality diagnostic, not a crystal ball.

Q: Is MEV protection worth paying for?

A: It depends on the expected extractable value and your risk tolerance. For small retail trades, the cost often outweighs benefits. For large swaps, time-sensitive arbitrage, or multi-step strategies, protection can save more than it costs. Always compare the expected loss from extraction to the explicit fees and implicit trust you accept by using a private relay or bundle service.

Q: How do I evaluate a wallet’s simulation quality?

A: Look for support of full call-graph simulation (not just the outer call), explicit gas and revert traces, recent-state execution (using a node synced to the latest blocks), and integration with the dApp intent so the simulation mirrors the exact transaction the dApp will broadcast. Bonus: wallets that let you re-run simulations with alternative mempool-ordering assumptions or simple adversary models offer richer decision data.

Q: Are private relays safe from censorship?

A: Private relays reduce public mempool exposure but centralize transaction routing; this introduces potential censorship or uptime risk. Safety depends on the relay’s governance, auditability, and whether there are transparent policies or multiple independent relays you can choose among. No relay is a complete substitute for decentralized market mechanisms.

Pool2 Farming Collapse: Why Uniswap-LP-Token Staking Programs Are High-Risk Compared to Direct Pool Participation

A liquidity provider deposits $50,000 into a Uniswap V3 pool, earning swap fees from traders. That straightforward arrangement has one contract risk: Uniswap itself. But a secondary market has emerged where farming protocols offer rewards for staking Uniswap LP tokens—nonfungible or ERC-20 position tokens that represent claims on pool liquidity. These protocols promise additional yields on top of swap fees, which sounds like financial progression. In practice, it layers a second contract and a second failure mode on top of the first.

The structural problem is not theoretical. Multiple Pool2 farming programs—initiatives that reward LP tokens from one DeFi protocol when staked into another—have experienced complete or partial fund loss. Smart contract vulnerabilities, rug pulls, and token devaluation have erased promised yields and sometimes principal. The difference between earning fees directly from a Uniswap pool and staking LP tokens into a farming contract is not merely a yield increase. It is a compounding of custody risk, contract risk, and price exposure that requires explicit understanding before deployment.

Diagram comparing direct Uniswap pool fee earnings with two-layer Pool2 farming reward structure showing additional smart contract risks

The difference between direct pool fees and farming rewards

When a user deposits assets into a Uniswap V3 pool, the protocol collects trading fees in proportion to the liquidity provided. Those fees are denominated in the pair’s two underlying tokens and accumulate inside the same pool contract. Withdrawing the position returns the original assets plus accrued fees, minus any impermanent loss from price movement. The entire process depends on one smart contract—Uniswap’s own pool contract—which has been audited, battle-tested across billions in volume, and operates according to publicly visible code.

A Pool2 farming arrangement works differently. Instead of collecting fees directly, the user stakes their Uniswap LP token into a separate farming contract operated by a third party. That farming contract watches the staked position and issues reward tokens—often a newly created governance or utility token—according to a programmed schedule. The user now controls two keys to two separate vaults. The first is Uniswap’s pool contract, which continues to function as designed. The second is the farming contract, which must perform its own logic correctly and must remain solvent long enough to distribute promised rewards.

The yield potential looks attractive. A Uniswap V3 pool might generate 5% to 20% annual fees depending on liquidity depth and trading volume. A farming protocol might add another 50%, 100%, or more in governance token rewards. But the farming contract is not a free addition. Every percentage point of additional yield requires the farming protocol itself to be sustainable. That means the farming contract must have a revenue source—either transaction fees, token inflation, or outside funding—and that source must be reliably allocated to reward distribution rather than misallocated, stolen, or exhausted.

The critical difference emerges when one layer fails. If Uniswap’s protocol suffers an exploit, users lose. If a farming contract suffers an exploit, users lose not only the farming rewards but potentially their staked LP tokens as well. The relationship is not additive; it is compounding. A user choosing between 10% direct fees and 15% total yield (5% fees plus 10% farming) is not choosing between 10% and 15%. They are choosing between one contract risk and two contract risks, plus the opportunity cost and operational friction of moving tokens between layers.

Impermanent loss applies to both layers simultaneously

Impermanent loss—the opportunity cost of holding a liquidity position when the pair’s price ratio diverges—affects the underlying LP token whether it sits in a wallet or in a farming contract. This is a critical point often missed in yield presentations. A farming protocol cannot shield a user from impermanent loss. It can only add rewards on top of it. If a user deposits $50,000 into an ETH/USDC pool when ETH is at $2,500 and ETH rises to $3,500, the position will have shifted toward USDC through rebalancing. The user will have profited less than if they had simply held ETH, and that opportunity cost is real regardless of farming rewards.

Farming rewards are denominated in the farming token, not in the pair being provided. If a farming protocol rewards in FARM tokens and FARM declines 50% while the user holds their position, the farming rewards have lost half their value. The underlying LP position may have recovered from impermanent loss through improved fees, but the reward token has independently devalued. This creates a situation where a user can experience impermanent loss on the underlying pair, devaluation of the farming reward token, and continued exposure to the farming contract’s continued operation—three separate risk surfaces that can all move against the user simultaneously.

A more complete risk model assigns weight to the probability of each failure. If a Uniswap pool has a 0.5% annual risk of serious exploit and a farming contract has a 5% annual risk—a reasonable assumption given that Uniswap has been extensively audited while many farming protocols have not—then the combined annual risk of losing funds due to contract failure rises from 0.5% to approximately 5.5%. That might still seem acceptable on paper, but it must be compared directly to the yield being offered. If the additional farming yield is 10% and the additional contract risk is 5%, then the expected value of the additional yield is already reduced by expected loss.

Custody exposure and token movement friction

Staking an LP token in a farming contract requires transferring custody from the user’s wallet to the farming contract. The user no longer holds the LP token directly; the farming contract holds it on their behalf. This is not the same as staking with a centralized exchange—the user retains control over the private key and can potentially withdraw without permission—but it does create a temporal custody exposure. During the time the LP token is staked, if the farming contract is compromised, the token is at risk even if the user’s wallet security is flawless.

This custody model also introduces friction that direct pool participation avoids. Withdrawing from a farming contract typically takes two transactions: one to unstake the LP token and another to collect the farming rewards. If the farming contract becomes insolvent or undergoes a migration, the user may face delays or unexpected restrictions on withdrawal. Several well-publicized farming collapses have locked user funds temporarily or permanently during the withdrawal process, even when the underlying assets were theoretically still available in the farming contract’s balance.

The movement of the LP token also creates decision friction. When a Uniswap position needs to be adjusted—removing liquidity, rebalancing into a different price range in V3, or exiting to manage impermanent loss—the user must first unstake from the farming contract, wait for confirmation, then execute the Uniswap transaction. This additional step creates operational complexity and may cause the user to delay necessary position management to avoid transaction costs.

From a DeFi protocol perspective, this friction also matters for risk management. If a user recognizes that impermanent loss is becoming severe and wants to exit the pool, the farming contract’s withdrawal mechanics should not slow the decision. Yet in practice, farming contracts often impose delays, locks, or withdrawal fees. A user might intend to exit a deteriorating position but abandon the plan because unstaking takes 7 to 14 days or incurs a 5% withdrawal penalty. The farming contract’s design may therefore force users to hold positions longer than they would choose independently.

The reward token devaluation trap

Farming rewards are issued as newly created tokens controlled by the farming protocol’s treasury or inflation schedule. These tokens have value only to the extent that they can be sold, used within an ecosystem, or exchanged for other assets. In many cases, farming tokens are created with the specific intention of being farmed, sold, and distributed to bootstrap a governance ecosystem. But if farming is the primary source of demand and most farmers immediately sell their rewards, the token supply can increase much faster than demand, leading to rapid devaluation.

This creates a timing trap. Early farmers in a Pool2 program might achieve 100% APY returns because farming is new and the reward token is scarce. Thirty days later, when the program is well-known and thousands of users have joined, the effective yield might be 20% because the token has devalued by 80% and the reward per unit has been diluted across more stakers. A user who deposits after seeing the 100% APY headline will not experience that return; they will experience whatever remains after dilution and devaluation. Yet the farming contract itself has already extracted value from the early participants and transferred it to later ones through token inflation.

Critically, the underlying Uniswap LP tokens cannot prevent this devaluation. The farming contract might have held $1 million in TVL (total value locked) during its first week and $500 million later. The farming token’s price might have moved from $100 to $1 in the same period. Users who staked during the growth phase are often holding a position that generates fewer rewards in real terms despite receiving more raw tokens, because the tokens are worthless. Some farming protocols address this through token buybacks or explicit sustainability mechanisms, but many do not, leaving users to discover the devaluation empirically by attempting to sell their rewards.

Smart contract vulnerability and liquidity provider exposure

Farming contracts are frequently written with less scrutiny than Uniswap’s core protocol. Many are deployed by new or small teams, audited by junior firms if at all, and then deployed to mainnet with millions in user funds. The attack surface is broad: reentrancy vulnerabilities in the reward distribution logic, integer overflow or underflow in accounting, unchecked access controls on administrative functions, or unsafe interactions with the underlying Uniswap protocol.

Several real-world examples illustrate the scope of this risk. A farming contract that fails to properly handle the return value from an ERC-20 transfer might silently lose user tokens while the contract’s accounting shows them as present. A contract that allows the owner to call an administrative function without timelocks might transfer all user funds to a personal wallet in a single transaction. A contract that fails to prevent flash loan attacks might be exploited to borrow enormous sums, manipulate prices, and liquidate the farming pool within a single block.

What distinguishes these failures from Uniswap exploits is that Uniswap’s code is extensively audited by multiple firms, maintained by a large core team, and protected by governance structures that mandate security reviews before upgrades. Farming contracts, by contrast, are often one-person operations with minimal review and no governance oversight. The typical farming contract developer is not incentivized to prioritize security above rapid deployment. Deploying before a formal audit allows the protocol to capture early farmer interest and justifies a higher token allocation to the founding team before the protocol’s value is widely known.

When a farming contract is exploited, users lose in multiple ways. The direct loss is the stolen or locked funds. The secondary loss is that the farming token becomes worthless or illiquid because the protocol is no longer operational. Users who were holding farming rewards for future sale discover that the tokens cannot be sold, and the remaining staked LP tokens may be unrecoverable if the contract’s withdrawal function has been compromised. This cascading failure means that staking LP tokens into a farming contract introduces tail risk that is not present with direct pool participation.

Legitimate alternatives: Direct fees, V3 concentrated ranges, and fee-tiering strategies

Uniswap’s native fee structure provides genuine yield without the layering of additional smart contract risk. V3’s concentrated liquidity feature allows users to choose tighter price ranges and earn higher fees on a smaller capital deployment. A user who might earn 5% on $50,000 in a broad range can potentially earn 20% on $10,000 in a narrow range around the current price, earning higher fees from the same trading volume while reducing impermanent loss exposure by concentrating capital where trading is most active.

Fee-tiering strategies—deploying capital across multiple fee tiers—allow users to serve different trading profiles. High-frequency traders might use the 0.01% tier. Volatile pairs might use the 0.30% tier. This native flexibility within Uniswap itself is controllable by the user, requires no additional contracts, and maintains alignment with the protocol’s core incentive structure. The user earns exactly what traders pay and no more, but that alignment reduces complexity and removes layers of intermediation.

For users seeking yield beyond native Uniswap fees, the risk-adjusted calculation should be explicit. A farming protocol offering 15% APY in addition to 10% pool fees is promising 25% total return. But that 15% requires the farming contract to remain operational, the reward token to retain value, and the protocol’s revenue model to sustain distributions. If the probability-weighted expected return from the farming component is only 5% after accounting for contract risk and token devaluation, the user is better served by deploying the same capital across multiple concentrated ranges in Uniswap itself, where control is complete and contract surface is minimized.

One accessible strategy is to route through a DEX protocol with native staking—such as participating in Uniswap’s own governance mechanisms or exploring protocols that share revenue directly with token holders—rather than seeking yield through third-party farming. Uniswap’s own fee-switch governance vote and potential revenue-sharing structures for UNI holders would provide yield without the intermediary layer. While this is not yet fully deployed, it represents a path toward yield that remains within the original protocol’s ecosystem and security model.

Risk assessment framework for evaluating farming opportunities

Before staking LP tokens into any farming contract, a user should audit several dimensions. First, what is the farming contract’s revenue model? If the protocol survives solely on token inflation and has no transaction fees, protocol revenue, or outside funding, then the farming rewards are a loan against future value creation. If that creation does not materialize, rewards will vanish. Second, who controls the contract? If a single developer can call administrative functions without governance approval or timelock delays, the protocol is one malicious decision away from total loss.

Third, has the contract been audited by a reputable firm, and is the audit report publicly available? An audit is not a guarantee—audits have missed critical vulnerabilities—but the absence of an audit should substantially increase the discount applied to promised yields. Fourth, what is the farming token’s liquidity and price history? If the token has traded for less than six months or has extremely low exchange liquidity, selling rewards might be impossible or would incur catastrophic slippage.

Fifth, what proportion of the farming contract’s TVL is held by the core team or early investors, and are those positions locked? If the founding team holds a large percentage of the farming token and can sell freely, the alignment between team success and user success is minimal. Sixth, what is the impermanent loss risk from the specific LP pair? A highly correlated pair like USDC/USDT has minimal impermanent loss but also minimal fees. A volatile pair like ETH/shitcoin has high impermanent loss that farming rewards may struggle to offset. The farming component should be evaluated only after the user has accepted the underlying pair’s risks.

The structural lesson: Yield requires risk, and risk compounds

The fundamental insight is that yields above native pool fees are never free. They must come from somewhere: token inflation, unsustainable treasury depletion, or external subsidies. Farming protocols often rely on the assumption that the farming token will appreciate, justifying the issuance of billions of new units. But token appreciation is not guaranteed and often contradicts the protocol’s economic model. If the purpose of farming is to distribute tokens and bootstrap adoption, then widespread distribution and the resulting supply increase will pressure price downward.

The secondary lesson is that risk compounds exponentially when multiple untested layers are stacked. A user accepting 5% additional yield in exchange for 5% additional contract risk has made a neutral trade on paper. In practice, contract risks are not independent. If the farming contract is compromised, it often forces an emergency withdrawal from Uniswap as well, introducing additional transaction costs and slippage. If the farming token collapses, the farming contract’s operational incentives may deteriorate, leading to worse withdrawal conditions.

The most durable approach to LP yield is to accept Uniswap’s native fee structure as the baseline and explore capital efficiency improvements within the protocol itself. V3’s concentrated liquidity, precise range management, and fee-tiering all provide yield enhancement without additional smart contract risk. A user who deploys $100,000 across five concentrated ranges in high-volume pairs and earns 15% annual fees through diligent management has achieved higher returns with lower risk than a user who locks the same capital into a farming contract promising 30% yield.

Hayden Adams and the Uniswap team built the underlying protocol to be resilient and transparent. Farming protocols built on top of Uniswap benefit from that foundation, but they do not inherit its security properties. The difference between earning fees directly from a Uniswap pool and staking LP tokens into a farming contract is the difference between running your own operation and delegating to a partner. The partner’s yields might be higher, but your exposure is also higher, and that exposure can materialize suddenly and completely.

Frequently asked questions

What is Pool2 farming and how does it differ from earning Uniswap fees directly?

Pool2 farming involves staking Uniswap LP tokens into a separate third-party smart contract that distributes additional reward tokens on top of Uniswap swap fees. Direct pool participation means holding LP tokens in your wallet and collecting only Uniswap’s native fees. Pool2 adds another contract layer, another failure mode, and custody exposure in exchange for higher nominal yields that may not reflect actual risk-adjusted value.

Does farming rewards protect against impermanent loss?

No. Impermanent loss is inherent to providing liquidity to any pair and occurs regardless of whether the LP token is held directly or staked in a farming contract. Farming rewards are simply additional tokens issued on top of the underlying position. If the pair’s price moves significantly, the LP position will experience impermanent loss first, and the farming rewards are applied to a potentially deteriorated position, not a protected one.

What should I evaluate before staking LP tokens into a farming contract?

Assess the farming contract’s revenue model, whether it has undergone formal audit by a reputable firm, who controls administrative functions and whether changes require governance voting, the farming token’s liquidity and price history, the core team’s holdings and lockup schedules, and impermanent loss risk from your specific LP pair. If the contract has not been audited or the team controls funds without oversight, the additional yield should be substantially higher to justify the risk.

MetaMask Phishing Kit Industry: How Scammers Clone Your Wallet Interface and What to Watch For

MetaMask’s dominance as a self-custodial wallet and Web3 gateway has made it a high-value target for phishing operations. The wallet’s simple, recognizable interface—the fox icon, the familiar input fields, the transaction approval screens—has been replicated thousands of times across malicious domains, cloned browser extensions, and fake mobile apps. Attackers have industrialized the process: they distribute phishing kits to lower-level scammers, maintain infrastructure that automatically generates lookalike sites, and deploy them across multiple channels simultaneously. A user who has used MetaMask for months can still fall victim if they land on the wrong URL after clicking a suspicious link or installing a counterfeit extension from an untrusted source.

The attack is not crude. Sophisticated phishing operations copy MetaMask’s exact visual design, replicate the Secret Recovery Phrase entry flow, and even simulate the wallet’s error messages. The goal is to extract a user’s Secret Recovery Phrase—the 12-word seed that grants complete control over every asset in the wallet—or to steal private keys before they are securely stored. Once that information is captured, the attacker has permanent, irrevocable access to the wallet and can empty it at will. Understanding the mechanics of these clones, the psychology they exploit, and the technical details that distinguish a real wallet from a convincing fake is essential for anyone holding cryptocurrency.

Comparison of genuine MetaMask interface with phishing clone, showing icon similarity and UI replication

The industrial structure of phishing-as-a-service

Phishing kit distribution has evolved into an organized, commercial operation. Attackers publish kits on dark web forums and encrypted messaging platforms, complete with documentation on how to deploy and customize them. A kit typically includes HTML templates that mimic MetaMask’s screens, JavaScript code that logs entered data to an attacker-controlled server, and deployment instructions for hosting on compromised websites or creating lookalike domains. The cost is low—often $50 to $200 for a functional kit—which lowers the barrier to entry and distributes the risk across many perpetrators.

The infrastructure layer is equally important. Attackers use domain registration services that accept cryptocurrency or stolen payment information, often in jurisdictions with minimal enforcement. They may register domains such as “meta-mask.io,” “metamask-wallet.com,” or “metamaskwallet.io”—variations that exploit visual similarity or sound-alike effects. Some kits include automated tools that monitor where the phishing links are clicked from and route traffic to slightly different fake pages depending on the source, the user’s device, or the time of day. This complexity is designed to evade automated detection and to ensure that security researchers and potential victims see different content.

Distribution channels have become more diverse. Email campaigns remain common, but attackers now rely on social media, Discord servers, Telegram channels, Reddit comments, and even compromised legitimate websites. A user searching “MetaMask download” or “how to import my wallet” may see a phishing link in search results due to SEO poisoning or paid ads that appear before the legitimate site. This concentration of effort means that even a careful user can be caught by a well-timed redirect or a believable recommendation from a compromised account.

The economic model works because the return is asymmetric. An attacker capturing a single high-value wallet—one holding $50,000 or more in cryptocurrency—generates more profit than the entire kit cost, even accounting for failed attempts and infrastructure expenses. The majority of victims may lose smaller amounts, but the aggregate result drives continuous innovation in deception and distribution.

Visual and functional cloning: where the deception becomes real

A sophisticated phishing clone does not simply copy a screenshot. It replicates MetaMask’s design system, including typography, color palettes, spacing, icons, animations, and interaction patterns. The UI framework may use the same open-source libraries that MetaMask itself uses, ensuring pixel-perfect consistency. Some clones even render the wallet’s distinctive animation sequences—the fox icon’s movements, the loading spinners, the fade-in effects—because these details build confidence that the user has reached the real thing.

The functional replication is more deceptive. A real MetaMask interface asks the user to enter their Secret Recovery Phrase during wallet recovery or import, but it never transmits that phrase to MetaMask’s servers; the phrase remains on the user’s device and is used only to derive cryptographic keys locally. A phishing clone performs the same visual flow—the same numbered fields, the same warnings about keeping the phrase secret, the same “continue” button—but it silently sends each word to an attacker’s server as soon as it is entered. The user sees no error, receives no warning, and believes the wallet is being restored. By the time they realize something is wrong, the attacker has already accessed their funds.

Even the error states are replicated. If a user accidentally enters the wrong words, a real MetaMask wallet shows an error message, often with helpful suggestions. Phishing clones copy these messages verbatim, preventing the user from detecting inconsistency. Some advanced kits will accept any 12 words and simply log them regardless of validity, whereas others validate the phrases against a list of known valid mnemonics to ensure they capture only valuable targets. The sophistication of this logic varies, but the goal remains: capture the Secret Recovery Phrase and disappear.

Mobile clones present a different but equally serious threat. A phishing app distributed via unofficial app stores or side-loaded through direct APK installation can ask users to import their wallet using a recovery phrase or private key. The app displays a MetaMask-like interface, requests the sensitive information, and transmits it to the attacker. Because mobile app stores have limited review processes for unauthorized distributions and users may not verify the app’s source, this vector has become increasingly active.

The psychological triggers that make phishing work

Phishing succeeds because it combines technical mimicry with psychological manipulation. The attacker creates a sense of urgency: “Your wallet needs an update,” “Your assets are at risk,” “Confirm your identity immediately.” These messages are deployed through email, social media, or in-app notifications, and they pressure the user to act quickly without thinking. A user who has experienced a previous scam or heard about network issues may be particularly vulnerable to a message claiming that immediate action is required to protect their funds.

Another trigger is social proof. Phishing campaigns often include screenshots of other users or testimonials claiming successful recovery or security updates. They may reference recent legitimate MetaMask announcements—a real security update, a new feature, a partnership—and misuse that context to justify asking for sensitive information. A user researching a real MetaMask issue may click on what appears to be official guidance but is actually a phishing domain registered by an attacker who anticipated the search query.

Authority exploitation is particularly effective. Attackers impersonate MetaMask customer support, claiming that the wallet needs to verify the user’s account due to suspicious activity or compliance requirements. The message appears to come from an official MetaMask email address or support channel, but it is actually sent from a spoofed address or a compromised account. A user who has previously contacted support expects to receive a response and is more likely to trust an email that mentions their wallet, their past interactions, or internal details that the attacker harvested from public information or past data breaches.

The final lever is convenience. A phishing message might claim to simplify recovery: “Don’t remember your phrase? We can help restore your wallet with just a few clicks.” This appeals to users who have lost access to their original wallet or want to consolidate multiple wallets. The attacker presents the clone as a legitimate tool, and the user enters their information believing they are solving a real problem.

Technical red flags that distinguish real from fake

The domain name is the first checkpoint. A legitimate MetaMask download comes from metamask.io or official app stores (Google Play, Apple App Store). Any other domain—including “meta-mask.io,” “metamask-download.com,” “official-metamask.io,” or anything with unusual TLDs—is potentially malicious. Users should type the URL directly into their browser rather than clicking a link from an email or social media, and they should verify the domain in the address bar before entering any information. Homograph attacks, which use visually similar characters (such as the Cyrillic “а” instead of the Latin “a”), can be difficult to detect, so hovering over the domain to confirm its spelling is a worthwhile habit.

Browser extension verification is equally critical. A real MetaMask extension displays a specific extension ID that can be verified on the Chrome Web Store or Firefox Add-ons site. The extension should only be installed from the official app store, not from a file downloaded from the internet or sideloaded into the browser. Once installed, users can right-click the extension icon, select “Manage Extension,” and confirm that it is published by “MetaMask.” Any mismatch—an extension from an unknown developer or one that requires suspicious permissions—should trigger immediate removal.

Mobile app verification follows the same principle. The real MetaMask app on Google Play is published by “MetaMask, Inc.” and has millions of reviews. On the Apple App Store, the publisher is listed as “Consensys” (the parent company). Users should check these details before downloading and should never sideload an APK file or install from third-party app stores unless they understand the risks. The app should also be downloaded at the moment it is needed, not preinstalled on a phone or stored in a folder that was transferred from another device.

Network behavior provides another layer of validation. A real MetaMask wallet never sends a Secret Recovery Phrase to external servers; it processes the phrase locally to derive keys and decrypt wallet data. A phishing clone must transmit the phrase somewhere, creating network traffic that can sometimes be detected with browser developer tools. Checking the “Network” tab in the browser’s developer console can reveal unexpected API calls or data submissions that a legitimate wallet would not make. Similarly, examining the source code in the “Elements” or “Inspector” tab may reveal logging statements, external script includes, or API endpoints that point to attacker-controlled infrastructure.

SSL certificate inspection is a foundational check. A legitimate website displays a padlock icon in the address bar and has a valid SSL certificate issued to “metamask.io” or a closely related legitimate domain. Clicking the padlock reveals the issuing certificate authority and the exact domain the certificate covers. A phishing site may use a valid certificate (because certificate authorities do not verify that a domain belongs to the intended organization), but it will be issued to a different domain. For example, a certificate for “metamask-security.com” is valid but does not belong to MetaMask. This mismatch is the indicator that matters.

What happens if you enter your Secret Recovery Phrase into a phishing clone

Once a Secret Recovery Phrase is compromised, the attacker has complete control over the wallet. They do not need a password, two-factor authentication, or the user’s device; they can import the wallet into any compatible tool (MetaMask, other Ethereum wallets, hardware wallets software, or even command-line tools) and access all cryptocurrency stored under that seed phrase. The attacker can see the user’s transaction history, view all connected accounts and assets, and approve any transaction without further permission.

The theft is often not immediate. An attacker with a phrase may monitor the wallet for a period, waiting to see when fresh deposits arrive or until the amount reaches a threshold worth the effort to drain. Some attackers use bots to continuously sweep any incoming funds. This delay can make the victim believe they entered the phrase into a legitimate wallet temporarily misconfigured, especially if they do not access that wallet frequently. By the time the user returns to check on their funds, they may find the balance at zero with no transaction history under their control.

Recovery from a compromised Secret Recovery Phrase is not possible in the traditional sense. The phrase itself cannot be changed because it is a mathematical seed that generates all the wallet’s accounts. The user’s only option is to create a new wallet with a new Secret Recovery Phrase and transfer any remaining funds to the new wallet as quickly as possible. If funds are being monitored by an attacker’s bot, even this transfer may fail if the attacker’s software moves faster. The lesson is that the Secret Recovery Phrase must be treated as the highest level of secret, never entered into any application except one that the user has personally verified as legitimate.

For a user who has already shared their phrase, the correct action is to immediately create a new wallet using a MetaMask wallet installed from the official source, then transfer all available funds to the new wallet’s address. This must be done from a device that has never been used to access the phishing site, or better yet, from a completely different device. If the attacker has already captured the phrase and the funds have been stolen, the transaction will fail; if the funds are still present, the user should assume the attacker has access and may drain the new wallet as well if additional secrets (such as a private key for the new wallet) are compromised by the same infection.

Prevention beyond awareness: practical defenses

Technical controls reduce exposure. Browser extensions such as MetaMask security plugins (not to be confused with phishing clones themselves) can warn users when they land on a known phishing domain by cross-referencing a database of reported sites. Some extensions also display a visual indicator confirming whether a website is legitimate. However, these tools are not infallible and should not replace manual verification; an attacker can register a domain faster than a blocklist can be updated.

Hardware wallets provide a stronger defense. A hardware device such as a Ledger or Trezor stores private keys in isolated hardware that cannot be directly accessed by software on a computer or phone. Even if a user is tricked into approving a transaction on a phishing site, the hardware wallet will display the details of the transaction (destination address, amount, network fee) on its own screen. The user can then verify that the destination matches their intention before physically confirming the transaction on the device. A phishing clone cannot override this verification process because it does not control the hardware wallet.

Behavioral practices matter as much as technology. Never enter a Secret Recovery Phrase into a digital device unless the user has personally confirmed the source through multiple verification methods. If a user must recover a wallet, they should do so on a freshly reset device used only for that purpose, ideally offline. Bookmarking the official MetaMask domain (metamask.io) and using the bookmark rather than searching or clicking links prevents typos and reduces the chance of landing on a phishing domain. Disabling browser notifications and email notifications from unknown senders removes one vector for phishing messages. Verifying any wallet recovery or security request through an independent channel—such as the official MetaMask support site or verified social media account—adds a friction point that deters many attackers.

For high-value wallets, a multi-signature or threshold approach offers protection. A wallet that requires approval from multiple devices or signers cannot be emptied by the compromise of a single Secret Recovery Phrase. This setup is more complex and requires planning, but it prevents a single phishing incident from resulting in total loss. Users with substantial holdings should seriously consider this architecture rather than relying on a single wallet and a single recovery phrase.

Emerging tactics and the evolution of the threat

Phishing operations continue to evolve. Some attackers now use deepfakes or AI-generated videos to impersonate MetaMask representatives in support conversations, increasing the perceived legitimacy of requests for sensitive information. Others use cross-platform campaigns, where a user is initially contacted on social media, then directed to a phishing site, then followed up with a “support” message offering help. This multi-stage approach exploits the user’s growing familiarity with the attacker’s narrative and their investment in the problem the attacker has created.

Infection via typosquatting and search engine manipulation has also become more sophisticated. Attackers register domains that are one character away from the legitimate site and invest in SEO to rank high in search results for keywords like “MetaMask download,” “import MetaMask wallet,” or “MetaMask Secret Recovery Phrase.” A user in a hurry may not notice the domain difference and may proceed with the installation or recovery flow before realizing the mistake.

Phishing kits are also becoming more selective. Rather than attempting to capture every phrase or key entered, advanced kits now use machine learning to identify which wallets likely contain high-value assets—by analyzing transaction history or account age—and target only those users with additional social engineering or follow-up attacks. This targeting reduces noise and noise-based detection, making the operations more efficient and harder to disrupt through honeypot data or fake input.

The industry is not static, but the fundamental attack surface remains the same: the Secret Recovery Phrase is the master key, and anyone who controls it controls the wallet. As long as users can be tricked into entering this secret into an attacker-controlled interface, phishing will remain effective. The sophistication of the clone is less important than the user’s verification of the source before entering any sensitive information.

Building a wallet security culture in high-risk environments

Organizations and individuals managing significant cryptocurrency holdings should establish operational security (OpSec) procedures that treat wallet recovery and Secret Recovery Phrase handling as the most sensitive operations. This includes creating the phrase in an isolated, offline environment; storing it in a physically secure location such as a safe deposit box; restricting knowledge of the phrase to only those who absolutely need it; and conducting regular, documented tests of recovery procedures without exposing the phrase itself to internet-connected devices.

For teams or organizations, multi-signature wallets and role-based access controls can distribute trust and prevent a single compromised team member or phishing victim from draining the treasury. A 3-of-5 multi-sig setup, for example, requires approval from three out of five key holders before any transaction is executed, making it impossible for a single attacker to steal funds unless they compromise three separate individuals and devices.

Regular security audits of the wallet setup, including verification of all connected devices, browser extensions, and access logs, help detect anomalies. If a large transaction is initiated from an unexpected address or time, or if the wallet is accessed from a new location, alerting team members and pausing operations can prevent loss. These practices are more important for institutional users, but the principles apply to individual users with substantial holdings as well.

Finally, maintaining skepticism of any unsolicited communication that requests wallet information, recovery phrases, or transaction approvals is the strongest defense. MetaMask will never ask for a Secret Recovery Phrase via email, social media, or support channels. If a message requests one, it is phishing, regardless of how legitimate it appears or how much technical detail it includes. A user who doubts the legitimacy of a communication should hang up, navigate directly to the official website independently, and verify the request through an official channel before taking any action.

Frequently asked questions

How can I verify that I am downloading the real MetaMask wallet?

Download MetaMask only from metamask.io, the Google Play Store (published by “MetaMask, Inc.”), or the Apple App Store (published by “Consensys”). Verify the domain in your browser’s address bar, check the extension ID or app publisher name, and never install from third-party websites or untrusted app stores. If you are unsure, navigate to metamask.io directly by typing the URL without clicking a link.

What should I do if I accidentally entered my Secret Recovery Phrase into a phishing site?

Immediately create a new MetaMask wallet from the official source on a clean device, then transfer all available funds to the new wallet’s address as quickly as possible. Do not reuse the compromised phrase. If the funds have already been stolen, contact the exchange or service where you received the funds to report the incident, though recovery is unlikely. Going forward, treat your Secret Recovery Phrase as the ultimate secret and never enter it into anything except a wallet you have personally verified as legitimate.

Can a hardware wallet protect me from phishing?

Yes. A hardware wallet stores your private keys offline and displays transaction details on its own screen for manual verification before any transaction is signed. Even if you are tricked into connecting to a phishing site, the hardware wallet will show you exactly what you are approving, and the attacker cannot override that verification. This is why hardware wallets are strongly recommended for holding significant amounts of cryptocurrency.

When to Use Multi‑Currency Firmware, a Passphrase, or Skip an Update: Practical Security Trade‑Offs for Trezor Suite Users

Picture this: you hold Bitcoin, Ethereum, and a handful of altcoins across several accounts. A new firmware notice lands in your inbox saying “critical vulnerability—update immediately,” but your desktop Trezor Suite shows your device as up to date. Do you update to universal firmware that supports all coins, switch to Bitcoin‑only firmware for a smaller attack surface, or pause and investigate? That concrete moment — juggling assets, device software, and a live threat notice — is where most of the tough decisions happen.

This article walks through the mechanisms behind multi‑currency support, passphrase protection (the hidden wallet), and firmware management as implemented in the official companion interface. I’ll compare the practical security trade‑offs, show where these defenses break down, and offer decision heuristics you can reuse. The aim is not cheerleading but to give a sharper mental model: what each choice changes in the threat equation, what it leaves exposed, and what to watch next.

Trezor device logo; illustrates the hardware component that isolates private keys and performs offline signing, central to firmware and passphrase security

How the pieces fit: device, firmware, Suite, and your node

At the core, a Trezor hardware wallet keeps private keys isolated inside the device and signs transactions offline. The Suite is the user-facing layer that prepares transactions, displays interfaces for multiple coins, and orchestrates firmware updates and authenticity checks. You can increase privacy and autonomy by connecting Suite to your own full node rather than Trezor’s default backend servers — that reduces metadata leakage and gives you control over chain data.

Firmware is the bridge between hardware and software features. Trezor Suite can install a Universal Firmware offering broad multi‑coin support, or a Bitcoin‑only firmware that intentionally leaves out non‑Bitcoin code to minimize the attack surface. Mechanistically, smaller firmware means fewer lines of code and fewer protocol implementations running on the device — fewer moving parts that can contain vulnerabilities. But smaller also means fewer native conveniences (staking, built‑in coin UIs, etc.) and more reliance on third‑party integrations for unsupported assets.

Multi‑currency vs. single‑purpose firmware: the trade‑offs

Mechanics first. Universal firmware includes parsers and transaction builders for many chains, which the device must validate before signing. That expands the device’s responsibilities: it must correctly parse a Solana or Cardano transaction format, enforce chain‑specific checks, and present clear human‑verifiable prompts. Bitcoin‑only firmware restricts the validation ruleset to UTXO logic and a handful of standards — simpler to audit and harder to misuse by a malformed transaction.

Trade‑offs to weigh:

– Attack surface vs. convenience: Universal firmware is convenient — native staking, built‑in UIs for ETH, ADA, SOL, and fewer external tools. Bitcoin‑only firmware reduces complexity and is a better choice if your priority is minimizing logical vulnerabilities. For users holding many tokens, the convenience loss may push you to accept a larger surface area.

– Third‑party dependency: If a coin drops out of native Suite support (deprecated assets like Bitcoin Gold or Dash), you must use third‑party wallets (Electrum, MetaMask, etc.) that integrate with your device. That reintroduces trust in external software for transaction construction and display, so the effective security depends on both the device firmware and the third‑party client’s security model.

– Staking and rewards: Native staking options let you delegate ETH, ADA, SOL securely from cold storage; moving to Bitcoin‑only firmware removes those native flows and may force you to use external tooling or hot wallets if you want to stake — an obvious liquidity and security trade‑off.

Passphrase (hidden wallet): mechanism, strengths, and surprising limits

The passphrase feature appends a user‑chosen secret word to your recovery seed, deterministically creating a separate, “hidden” wallet. Mechanically it’s elegant: the seed plus passphrase produces an independent deterministic key tree. If an adversary has your physical seed, they still can’t derive the funds in the hidden wallet without the passphrase.

Strengths:

– Effective against physical compromise of the seed or backup copies.

– You can run multiple hidden wallets by changing the passphrase — useful for plausible deniability or compartmentalizing funds.

Limitations and failure modes:

– The passphrase becomes a single point of complete failure. If you forget it, funds are irrecoverable. If you type it on a compromised host when unlocking, it can be intercepted. The human element — remembering a complex, high‑entropy phrase — is the real security bottleneck.

– If you reveal the existence of the hidden wallet (for example, by using it frequently on a device linked to observable addresses, or by backup practices that hint at multiple wallets), you can erode the plausible deniability value.

Practical heuristic: treat the passphrase as an independent secret stored separately (and ideally offline) from the recovery seed. Use a password manager or a physical cipher that you can reliably reproduce under stress, but avoid storing the passphrase in the same place as the seed backup.

Firmware updates: urgency, verification, and the recent delivery confusion

Firmware updates patch vulnerabilities and add features, but they also alter the device’s attack surface. The safe pattern is: when a vendor issues an update, verify it through the official Suite and your own checks (e.g., release notes, signatures). Trezor Suite is designed to manage firmware authenticity checks before installation, reducing the risk of a malicious image reaching your device.

Two practical headaches to watch: delivery lag and mixed messaging. A recent community thread noted that users received emails about a critical 2.9.0 firmware while Suite reported their firmware as up to date at 2.8.10. That kind of mismatch can create panic: should you force an update, or wait to avoid a mismatched or incomplete rollout? The correct approach is cautious verification — confirm the vendor announcement in the Suite’s release page, check official channels, and if necessary, contact support rather than blindly installing a file from an unknown source.

Decision rule: if the update addresses an actively exploited vulnerability, prioritize updating quickly but only through Suite’s verified flow. If Suite shows a discrepancy, prefer out‑of‑band confirmation (official blog, known support channels) before applying any manually downloaded firmware image.

Putting it together: a decision framework for common user profiles

Below are simple heuristics based on typical user priorities. They’re not rules, just trade‑off maps to sharpen choices.

– Maximal safety, Bitcoin‑centric: Install Bitcoin‑only firmware; enable Coin Control; use a personal Bitcoin full node for Suite connections; avoid passphrase complexity unless you have a robust recovery plan.

– Multi‑asset long‑term holder who values convenience: Use Universal Firmware to keep native staking and built‑in support; enable passphrase protection for a high‑value hidden wallet; use Suite’s Tor switch and, when possible, a custom node or trusted backend for high‑privacy flows.

– Power user with high privacy needs: Run your own full node; use Bitcoin‑only firmware for on‑chain BTC; manage non‑Bitcoin assets through audited third‑party wallets that integrate with the device; keep passphrases in an air‑gapped manager.

Where these controls break down and what to watch next

No single setup is invincible. Key failure modes: user error (lost passphrase), social engineering (fake Suite clones or phishing emails), and supply‑chain attacks (compromised firmware distribution). Add to that platform differences — Android allows full transactional support; iOS is mainly portfolio tracking unless you have a Bluetooth model — and you get an operational surface that changes with device and OS choices.

Signals to monitor in the near term: mismatch reports between vendor emails and Suite delivery (as seen this week) are a red flag indicating either rollout issues or communication gaps. Also watch deprecation notices for low‑demand coins; if your coin drops native support, examine which third‑party wallets remain trustworthy and what functionality you lose (for example, native staking).

FAQ

Should I always install the latest universal firmware?

Not necessarily. You should install the latest firmware when it patches a real vulnerability you’re exposed to, but prefer the Suite’s verified update path. If you primarily use Bitcoin and prioritize a minimal attack surface, consider Bitcoin‑only firmware. If you hold many tokens and rely on built‑in staking, universal firmware is likely more practical. Confirm critical patches through official channels if Suite’s signals are inconsistent.

Does a passphrase make a Trezor wallet unbreakable?

No. A passphrase greatly raises the bar against physical seed compromise, but it introduces other risks: loss of access if forgotten, interception on compromised hosts, and operational mistakes that reveal hidden wallets. Treat the passphrase as a high‑value secret that must be stored and used with the same discipline as the seed.

What if my coin is deprecated in Suite?

Deprecated coins often remain accessible through third‑party wallets that support Trezor integration. That means you trade native convenience for reliance on external software. Evaluate the third party’s security track record, prefer open, audited clients when possible, and keep in mind that a deprecated coin may lack future Suite security protections like scam detection or MEV shielding.

Is connecting Suite to my own node worth the effort?

For privacy and sovereignty, yes. Running your own full node reduces metadata leakage and gives you independent verification of chain state. The trade‑off is operational complexity — node maintenance, storage, and uptime. For many US users with privacy concerns this is a sensible step; for casual users the built‑in backends may be an acceptable convenience trade.

Final practical note: if you want a single place to explore features, connection options, and the Suite update flow before making changes, check the official interface and documentation to avoid phishing traps — for navigation and resources, start with trezor suite. The core idea to walk away with is this: every convenience feature — multi‑coin firmware, native staking, or passphrases — carries a measurable change in the threat model. Make that model explicit before you switch modes, and keep a recovery and verification plan ready.

BGK24 i BGK konto: porównanie mechanizmów bezpieczeństwa i wybór rozwiązania dla firm

„Jedno urządzenie, jedna tożsamość” — to krótkie hasło dobrze oddaje zasadniczy kontrast w projektowaniu BGK24: z jednej strony wygoda i integracje dla firm, z drugiej restrykcyjna architektura bezpieczeństwa, która redukuje powierzchnię ataku kosztem elastyczności. Ten artykuł porówna kluczowe mechanizmy logowania i autoryzacji w BGK24, wskaże typowe punkty ryzyka dla przedsiębiorstw oraz zaproponuje praktyczne heurystyki decyzji przy wyborze modelu dostępu i zabezpieczeń.

Na wstępie ważne: BGK24 to nie tylko „aplikacja do przelewów” — to platforma z funkcjami od SIMP dla masowych wypłat, przez integracje Web Service z ERP, po obsługę rachunków VAT i split payment. Równocześnie mechanizmy autoryzacji (token mobilny, SMS, biometryka) i operacyjne ograniczenia (np. jedno aktywne urządzenie na profil) determinują realne możliwości operacyjne i ryzyka dla firm korzystających z kont prowadzonych w BGK.

Schemat ilustrujący równowagę między wygodą integracji a ograniczeniami bezpieczeństwa w systemie bankowości BGK24

Jak działa logowanie i autoryzacja w BGK24 — mechanika i konsekwencje

Podstawowy mechanizm: dostęp do BGK24 łączy tradycyjne uwierzytelnienie (login + hasło) z drugim czynnikiem. Główne opcje drugiego czynnika to aplikacja BGK24 Token (generująca kody offline), autoryzacja SMS oraz logowanie biometryczne w aplikacji mobilnej. Każde z tych rozwiązań ma inną dynamikę ryzyka i użyteczności:

– Token mobilny (BGK24 Token): generuje kody bez dostępu do sieci po aktywacji — to istotna zaleta w warunkach słabego zasięgu i przy atakach na kanały komunikacyjne. Mechanizm redukuje ryzyko przechwycenia kodu w tranzycie, ale wprowadza operacyjną zależność od urządzenia: użytkownik może aktywować profil tylko na jednym smartfonie, co utrudnia szybkie delegowanie uprawnień między pracownikami.

– Autoryzacja SMS: prostsza w wdrożeniu i użyteczna jako zapasowa metoda, ale obarczona znanymi słabościami (przejęcie numeru przez SIM-swap, podsłuch u operatora) — nadaje się do niskiego i średniego ryzyka operacji, nie do transakcji masowych bez dodatkowych kontroli.

– Biometria: użyteczna na poziomie logowania do aplikacji mobilnej — zwiększa komfort i ogranicza ryzyko ujawnienia hasła, lecz nie zastępuje procesów audytu i autoryzacji transakcji na poziomie instytucjonalnym (np. zatwierdzania wypłat SIMP).

Porównanie trybów: bezpieczeństwo kontra operacyjność

Rozważmy trzy typowe scenariusze firmowe i które mechanizmy BGK24 są najlepiej dopasowane:

– Mała firma z jednym księgowym: prostota i redundancja są priorytetem. Kombinacja hasła + SMS + limity transakcji domyślnie (1 000 zł dziennie, 500 zł pojedynczo) może wystarczyć, pod warunkiem jasnej procedury zmiany numeru i szybkie podwyższenie limitów przez bank, gdy zachodzi potrzeba.

– Średnia firma z ERP i zautomatyzowanymi płatnościami: integracja Web Service i SIMP (lub SIMP Premium) stawiają wymóg silnych reguł autoryzacji i audytu. Tu token mobilny lub dedykowane mechanizmy podpisu elektronicznego, plus wielostopniowe uprawnienia w systemie ERP, lepiej zabezpieczą masowe przelewy. Trzeba jednak pamiętać o ograniczeniu „jednego smartfona” — w praktyce wymusza to precyzyjną politykę roli i awaryjnego dostępu.

– Instytucjonalny odbiorca środków rządowych: wymagana jest zgodność, ślad audytowy i odporność na manipulacje. BGK24 wspiera obsługę programów rządowych i integrację z e-Administracją (Profil Zaufany, MojeID), co ułatwia formalne procesy, ale nie zwalnia z wdrożenia wewnętrznych procedur kontroli praw dostępu i rotacji uprawnień.

Gdzie system BGK24 łamie się praktycznie — ograniczenia i pułapki

Mechanizmy BGK24 są solidne, lecz nie są uniwersalnym panaceum. Oto kilka ograniczeń, które często pojawiają się w praktyce:

– Single-device binding (jedno urządzenie na profil): to dobra praktyka z punktu widzenia bezpieczeństwa, ale tworzy punkt awarii. Utrata telefonu przez osobę mającą kluczowe uprawnienia może wstrzymać operacje. W procesie zmiany urządzenia trzeba usunąć stary telefon z listy autoryzowanych, co bywa problematyczne przy braku natychmiastowego wsparcia operacyjnego.

– Mechanizm blokady po trzech błędnych logowaniach: zapobiega brute-force, ale może być użyty jako narzędzie DoS przeciwko funkcjonowaniu firmy (atak celujący w konta kluczowych użytkowników). Odblokowanie wymaga kontaktu z infolinią — plan awaryjny jest więc konieczny.

– Limity transakcji domyślne i ich podnoszenie: domyślne limity są konserwatywne (1000 zł/ dzień), a proces ich zwiększania (do 50 000 zł) wymaga procedur i weryfikacji, co może opóźnić operacje o charakterze pilnym.

Praktyczne heurystyki dla decydentów IT i finansów

Na podstawie mechanizmów opisanych powyżej proponuję proste reguły decyzyjne:

– Zarządzanie dostępem: traktuj jedno urządzenie jako „klucz sprzętowy”. Planuj rotację i backup: przypisz co najmniej dwóch uprawnionych użytkowników do krytycznych funkcji z jasno zdefiniowanym planem awaryjnym (procedura usunięcia starego telefonu i parowania nowego).

– Poziom autoryzacji a wartość transakcji: stosuj token mobilny lub procesy wielostopniowe dla transakcji o wysokiej wartości/masowych (SIMP). Dla niskich kwot rozważ SMS, ale zabezpiecz numer telefonu i stosuj monitorowanie anomalii.

– Integracja z ERP: używając Web Service dla automatyzacji, wprowadź mechanizmy kontroli po stronie ERP (separacja obowiązków, dwuetapowe zatwierdzanie) — samo API nie eliminuje potrzeby kontroli wewnętrznej.

Co warto obserwować w najbliższych miesiącach

BGK w ostatnim okresie zwiększa skalę działań międzynarodowych i inwestycji (m.in. porozumienie z Saudi Export-Import Bank i inwestycja w fundusz private debt), a także rozwija ofertę dla regionów (programy wsparcia dla samorządów). Dla użytkowników BGK24 sygnały te oznaczają większe natężenie transakcji międzynarodowych i potencjalne rozszerzenie funkcji platformy. Obserwuj jednak zmiany regulacyjne i ogłoszenia BGK: nowe produkty finansowe mogą wymagać aktualizacji procedur KYC, zmian w integracjach Web Service oraz adaptacji polityk bezpieczeństwa.

Jeżeli chcesz szybko przejść do praktycznego logowania lub odświeżenia uprawnień, skorzystaj z oficjalnego przewodnika i punktów dostępu do logowania: bgk logowanie.

FAQ — najczęstsze pytania praktyczne

Co zrobić, gdy kluczowy użytkownik straci telefon z aktywnym tokenem?

Najpierw zadzwoń na infolinię BGK i zgłoś incydent, następnie przeprowadź procedurę usunięcia urządzenia z listy autoryzowanych i sparowania nowego telefonu. Równolegle aktywuj plan awaryjny: przekaż uprawnienia zastępcze zdefiniowane wcześniej (inny użytkownik z uprawnieniami lub tymczasowe uprawnienia przy zachowaniu zasady separacji obowiązków).

Czy SMS jest bezpieczny do autoryzacji wysokich płatności?

SMS można traktować jako metoda zapasowa, ale nie jako jedyny kanał dla wysokich lub masowych płatności. W praktyce zagrożenia typu SIM-swap i podsłuch sprawiają, że dla transakcji o dużej wartości lepszym wyborem będzie token mobilny lub wielostopniowa autoryzacja z kontrolą po stronie ERP.

Jak BGK24 wspiera integrację z systemami księgowymi?

BGK24 oferuje Web Service API, które umożliwia integrację z systemami ERP i księgowymi. To pozwala na automatyzację zleceń płatniczych i odczytu sald, ale wymaga implementacji kontroli procesów (np. podwójne zatwierdzenie w ERP), śladu audytowego i ochrony kluczy API.

Jak działają limity transakcji w aplikacji i czy można je zmienić?

Domyślnie aplikacja ma limity 1 000 zł dziennie i 500 zł na pojedynczy przelew. Można je podnieść maksymalnie do 50 000 zł, ale proces wymaga weryfikacji i zgłoszenia do banku. Planuj podwyższenie limitów z wyprzedzeniem, bo procedura może trwać.

Muscarici Fly Casting Open edition 3

MCO309


Muscarici Fly Casting Open editia 3, a avut loc in Sag (Timisoara) in 14 Mai 2016, ( o locatie deja cunoscuta a acestui eveniment ).
Aceasta editie ia avut ca instructori invitati pe:
Djordje Andjelkovic IFFF MCI, THCI, E L1, Serbia. Barrio Pro Team, Nor-Vise Fly Tying Pro Team,
Sasa Zec EFFA CI, Serbia
Vladimir Glamocak Swiss CDC Team member Serbia

O zi dedicata casting-ului, sub indrumarea lui Djordje Andjelkovic si Sasa Zec, in care am sustinut Openul si am beneficat de prezentarea lui Djordje de pescuit la uscata cu fire de clasa mica level si DT specifice pentru nimfa, pe lansete EvilFly, la pescuit cu musca uscata.

Desi a fost o zi cu vreme nu foarte buna, cu vint destul de intens, Openul s-a sustinut cu toate probele sale. S-a inceput cu proba de precizie, si apoi cu proba de distanta. Dupa finalizarea Openului s-a facut prezentarea de catre Djordje cu seria de lansete Evilfly pe care le produce. Apoi s-au mai incercat lansete si fire de tot felul pina cind vremea ne-a alungat spre restaurantul DAF din Giroc unde am stat la povesti pina seara. Am discutat cu Djordje ca in toamna sa facem o tabara de instruire pentru cei care doresc sa candideze pentru a fi instructor de casting, iar apoi sa vedem anul viitor sa organizam primul examen de instructori IFFF din Romania. Sasa Zec va sustine cu ocazia asta examenul de MCI.

Clasamentul final:
Proba de precizie:
Loc I – Mihnea Popescu cu 30 puncte
Loc 2 – Luca Moga cu 25 puncte
Loc 3 – Petru Galescu, Pavel Inclezan si Titus Nicoara cu 15 puncte

Proba de distanta:
Loc 1 – Titus Nicoara cu 29.90 m
loc 2 – Mihnea Popescu cu 29.65 m
Loc 3 – Luca Moga cu 28.25 m

Au fost prezenti la eveniment 27 de muscari din Baia de Aries, Deva, Hunedoara, Caransebes si Novi Sad, din care au participat la competitie 14.

Parteneri: Clinica de Bere, Ceradez, Ideatm, Idesign, BNB.

Muscarici Casting Meeting Giroc

GirocDec2015-00

Simbata 19.12.2015 la Sala de sport din Giroc a avut loc intinirea de casting a Muscaricilor, intilnire ce a avut ca scop incheierea anului 2015 cu bine si pregatirea de actiuni viitoare.

Datorita timpului nefavorabil, am folosit sala de sport a Scolii din Giroc multumita lui Boris Babici care a facilitat accesul. La intilnire au fost prezenti Peti Bolodovina si Dan Almasan din Deva, Dan Olescher mebrul al Clubului Muscarilor Baia de Aries, Liviu Hoanca membru al Clubului Musca 13 Sibiu, si Muscarici.
A fost o intilnire dedicata casting-ului in care s-au folosit o mutime de lansete si fire de la diversi producatori, de diferite clase de la 2 pina la 9 DH. Timp de 5 ore am avut sala la dispozitie si am folosit intregul timp pentru a testa lansete si a controla firul in aer.
Am participat cu aceasta ocazie si la actiunea caritabila initiata de un grup de profesori ai scolii din Giroc, pentru a ajuta o familie sarmana cu un copil cu sindrom Dawn, ce traieste intr-un sat din imprejurimile Timisoarei, actiune ce are ca scop asigurarea lemnelor pentru incalzire pe toata durata iernii.

Dupa casting-ul din sala de sport ne-am retras la DAF junior pentru o bere si discutii, pentru a stabili intilnirii viitoare.
A fost o zi foarte OK cu mult casting si dezmortit de fire, o intilnire placuta cu prieteni vechi.
Astfel ne-am finalizat anul cu bine, an dedicat castingului, cu citeva actiuni notabile:

  1. Editia 1 a Muscarici Fly Tying Days, editie cu prezenta online a lui Davie Mc Phail,Timisoara, Castel Royal  20.03.2015
  2. Editia 2 a Muscarici Fly Casting Open, competitie cu prezenta nationala, Sag 18.04.2015
  3. Curs de initiere in Fly Casting la Scoala din Giroc in cadrul Scoala altfel, Giroc 22.04.2015
  4. Editia 8 A Muscarici Fly Casting Days, Retezat Pensiune Dumbravita 25.06.2015 cu prezenta a 6 instructori acreditati: Lasse Karlsson, Pual Arden, Thomas Berggren, Djordje Andjelkovic, Sasa Zec, Paul Sas.
  5. Intilnirea de casting Giroc de acum.

Multumim tuturor celor care ne-au fost alaturi in acest an, au fost prezenti la actiunile noastre. Multumim celor care ne-au sprijint si fara de care actiunile noastre nu ar fi reusit.

Va uram tuturor Sarbatori Fericite, si un an Nou mai Bun.


Muscarici Fly Casting Days editia 8

MCD8w14Event feedback:    (English below)

http://www.flyfishingromania.com/blog/this-summers-adventure-part-3/

Muscărici Fly casting Days, ediția 8 – 26-28 iunie 2015, Rîul Mare Retezat, un eveniment de top, cu participare internațională, cu instructori invitați de excepție

http://www.pescuitlamusca.ro/blog-2/files/6c7749912e1860fdb805e14c978556b5-128.html

 http://www.replicahd.ro/?p=20808

http://www.arad24.net/2015/07/01/muscarici-fly-casting-days-editia-8-26-28-iunie-2015-riul-mare-retezat-un-eveniment-de-top-cu-participare-internationala-cu-instructori-invitati-de-exceptie/banner
 

https://www.facebook.com/100000873342176/videos/vb.100000873342176/949940578378378/?type=2&theater

https://www.facebook.com/100000873342176/videos/vb.100000873342176/949925791713190/?type=2&theater

https://www.facebook.com/100000873342176/videos/vb.100000873342176/949919875047115/?type=2&theater


Povestea evenimentului asa cum o stiu eu…

Dupa o lunga perioada de pregatiri a sosit ziua intilnirii cu instructorii invitati, joi 25 iunie 2015 am plecat dupamasa spre aeroport sa-i intimpinam pe Lasse si Thomas, ca de acolo sa mergem la Castel Royal din Timisoara si sa ne intilnim la o masa cu Paul si Djordje. Zis si facut, am ajuns cu ei la Castel si in scurt timp Bogdan Carpenisan l-a adus pe Paul de la intrarea in oras, si Boris Babici l-a adus pe Djordje.
Am avut o masa linisitita si ne-am pornit pe drum spre Riul Mare. Coloana de 3 masini, pline cu bagaje si de toate pentru eveniment. Ne-am oprit in Lugoj ca sa facem plinul la masini si am plecat spre Sarmizegetusa cu scopul de a vedea in ce masura e buna arena romana pentru castingul de noapte cu fire luminiscente. Ajunsi acolo pe noapte deja ne-am plimbat intre ruine sa vedem care este locul cel mai potrivit, ne-am hotarit la Forum in cazul in care timpul ne va permite sa venim pina aici simbata seara. Am ajuns la pensiunea Dumbravita unde era asteptati de sotii Ardac din Bucuresti si de Smaranda si Liviu Neagoe din Germania, pentru a incepe discutiile cu privire la proiectul lor de renaturare a riului Ses. Cu berea Caster si povesti, s-a facut noapte tirziu pina am ajuns sa ne culcam.

Vineri 26 iunie dimineata, devreme au sosit prietenii nostri din Deva, Peti si Dan; ne-am ocupat de amenajarea locului pentru eveniment si am pornit intr-o recunoastere pe vale in sus, ca se le aratam instructorilor locurile pe care le vom putea pescui zilele viitoare.
Am mers la barajul Gura Vaii, si de acolo am intrat pe Lapusnicul mare, trecind de Rotunda pentru a vedea cum e apa. La prinz ne-am intors la pensiune si dupa un prinz bun, ne-am apucat de pornirea evenimentului. A venit deja multa lume, si incep si vestile despre intirziati, dintre care una neplacuta in privinta lui Valeriu Sepi din SIngapore, care venind cu masina dinspre Timisoara spre eveniment, a avut un accident usor in Topolovat si a trebuit sa renunte la participare.
Ne-am intilnit cu participantii din Chisinau pe care eram curios sa ii intilnesc, pentru ca s-au inscris din start la sectiunea DH, si dupa prinz, am inceput sa aranjam pornirea evenimentului.
Dupa o scurta prezentare a instructorilor a urmat prima demonstratie de casting a lui Lasse, demonstratie foarte interesanta ce s-a axat pe demontarea celor mai cunoscute mituri in casting, prin exemplificarea lor, astfel diferente intre actiunile betelor in casting la distanta, “anchor is charging the rod”, diferenta de clasa ca plus in atingerea unei lungimi de casting mai mari, pe rind ne-am distrat intr-un fel dar am invatat foarte multe din asta.
Dupa incheierea demonstratiei, s-a pornit partea de workshop-uri pe sectiuni si eu, am plecat cu Thomas si Djordje pe coada lacului Ostrov unde ne intilneam cu participanti sectiunii DH. Ne-a plouat continu dar toti am fost pe apa in wadersi, bine echipati si am inceput sa lucram la lucruri simple dar care sint baza oricarui tip de casting in DH: lift off, anchor set, single si double Spey, “the Bloody L”. Am incercat mai multe lansete cu fire diferite, de la un scandi head scurt, la fire cu head lung pentru spey. A fost prima confruntare cu sisteme diverse si am incercat sa vedem avantajele fiecaruia dintre ele. Scandi heads de la Airflo, foarte bune si moi, iar fir de spey de la Barrio pe care l-a adus Djordje. Instructorii au lucrat individual cu fiecare dintre participanti.

S-a facut seara si am plecat spre pensiune pentru cina, urmand ca dupa aceasta sa pregatim primele conferinte sustinute de Thomas si Lasse. Thomas a prezentat conceptul brandului sau Zimsen cu gama de lansete si fire, apoi a prezentat o parte din testarile si calcule facute pentru crearea acestor lansete. A fost o conferinta foarte interesanta sustinuta cu scheme si grafice in ideea de a vizualiza cit mai bine tipurile de teste care se fac, coeficientii obtinuti si ce semnifica acestia, in ce mod ne ajuta sa intelegem ce face o lanseta.
Lasse a facut o prezentare a noutatilor brandului ECHO, fiind prezente lansetele Echo Boost si Glass, lansete cu actiune total opusa dar care au fost mult mai usor intelese, caci Glass este un tip de lanseta gindita pentru nostalgicii perioadei de inceput a fibrei de sticla. Sincer mi-am dorit sa inteleg mai bine optiunea pentru lansetele astea asa de moi, si am vrut sa incerc modelele pentru DH.
Seara s-a lasat cu multa bere Caster Intensive, exceptionala de altfel, si vinuri Ferdi pina in noapte tirziu.

Simbata 27 iunie, a inceput la ora 10 cu demostratia lui Thomas legata de actiunea lansetelor si profilul firelor, in ce masura conteaza acestea. A fost o ora care a completat conferinta din seara trecuta. Toata aceasta demostratie s-a axat pe “Rod Action Paradox”. Dupa aceasta s-a ramas pe iarba pentru workshop, si testat de lansete si fire. A urmat demostratia lui Sasa despre “Trick Casts” demonstratie in care au fost prezentate varinate de rich cast, curve cast, presentation cast.
Am stabilit ca dupa prinz iesim cu totii pe coada lacului Ostrov si acolo a inceput demonstratia lui Paul Arden despre “Improving core skills”, demostratie ce a urmat unui moment de continuare de Water Cast sustinuta de Sasa. Ne-am intilnit si cu Gabi Culda, din Riul de Mori, cel de la care luam autorizatiile de pescuit cind sintem in zona, si am vorbit multe despre ce si cum putem face pentru apele din zona, si cum am putea sa le fin de ajutor rangerilor de aici.

Demo-ul lui Paul a fost foarte interesant in sensul ca ne-a prezentat diferite variante de a face un anumit tip de cast dupa cei care le-au dezvoltat si le aplica in situatii speciale, astfel Curve Cast facut prin aplicarea  unui stop foarte ferm din lansarea pe lateral, mendinguri facute prin punere unei parti din fir ingramadit intr-un vas, tot felul de nebunii. Noi cei de la DH am continuat cu Lasse si Thomas patrea de Double Spey si Snake Roll Cast. Am lucrat pe lac avind un timp frumos, si cald.
Seara in timp ce lumea a plecat pentru cina, i-am luat pe Lasse si Thomas si am urcat pe dealul deasupra Clopotivei, pentru a le arata muntii si intreaga vale, fiin un loc cu privelisti superbe. Ne-a prins o ploie scurta acolo, si in timp ce ne uitam la peisaj, totul se schiba cu repeziciune. A fost o experienta foarte OK, mai ales ca doream sa vada mai bine unde sint si ce poate oferi tara Hategului.
Ne-am intors la pensiune si dupa cina, ne-a, pregatit pentru conferintele de seara, am avut o scurta discutie cu reprezentatii cluburilor din FRPMA, care a avut ca principal subiect, bulibaseala data de lupta dintre FRPSC si AGVPSR legata de competitiile de pescuit, si lipsa de activitate in federatie.
Djordje a prezentat scurt seria de fire de la Barrio, dupa care ne-a prezentata lansetele de nimfa Evil Fly, realizate de el, lansete de clasa 2-3-4 de 10 si 11 picioare, lansete pe care am avut sansa sa le pescuiesc zilele ce au urmat.
Dupa prezentarea asta, Lasse, Thomas si Paul Arden ne-au povestit lucruri despre campionatele mondial de casting, echipe de casting si din punctul lor de vedere ce ar trebui facut sa incepem si noi in a ne forma o echipa reprezentativa de casting. Au fost lucruri interesante de aflat. Intre timp eu am fugit cu Paul Arden afara sa pregatin sesiune de casting nocturn, ce s-a tinut pe pajistea din spatele pensiunii, fiind mai aproape si mai intunecata decit situl de la Sarmizegetusa. I-am prezentat charger-ul de lumina pe care l-am facut pentru asta, si l-am testat pentru a fi siguri ca totul e OK, bineinteles ca imediat dupa testare, firele de alimentare s-au rupt asa ca am improvizat sa putem sa-l folosim pe pajiste, caci lumea se aduna deja.
Am avut la dispozitie 3 fire Thunderbolt Luminous de la Sexyloops, si le-a incarcat in masina adusa special pe pajiste, asa ca ne-am jucat cu ele tirziu in noapte. A fost o experienta foarte interesanta, si a fost cumva regalul serii.

Duminica 28 iunie, de dimineata s-a pornit cu demostratie lui Djordje despre casting cu muste mari si grele, a fost o demonstratie dedicata pescuitului la stiuca si pesti mari. Dupa asta, s-a impartit lumea pe sectiuni iar cu Djordje si Thomas am plecat spre lac pentru ultima parte a workshop-ului. Am facut casting cu lanseta lui Thomas de competitie, 18 picioare, si fir cu head de 27 metri, lanseta care punea mari probleme in a ridica firul din apa, pe linga asta am facut casting cu lanseta Swich de la Echo, Glass de clasa 6 si 11 picioare, o lanset care m-a impresionat ca actiune cu un scandi head greu. Am repetat castingurile invatate si la ora 13 ne-am indreptata spre pensiune pentru a face concursul de casting programat. Intre timp Paul Arden a facut o demostratie pe iarba despre care am auzit ca a fost exceptionala, si cind am ajuns deja era incheiata.

Ne-am pus sa aranjam locatia de casting, si impreuna cu instructorii am hotarit ca e mai bine sa facem o competite neoficiala ce sa contina numai o proba de distanta, cu echipamentul dorit de fiecare, dar care sa destinda un pic toata lumea, in sesnul in care sa o folosim pentru a distra un pic impreun cu instructorii. Zis si facut, am amenajat pajistea, si s-au inscris 10 participanti si cei 6 instructori intr-o sectiune separata.

Eram presati de timp, astfel ca dupa o lansare de test, s-a trecut la lansari masurabile, cit mai multe in decurs de 1 minut. A fost super interesant pentru ca media lansarilor in acest minut a fost de 4. astfel la finalul sectiunii de participanti Alex Moga  a avut cea mai lunga lansare de 28.3 m, ocupind locul 1, Luca Moga cu 27.2 m a ocupat locul 2 si Titus Nicoara cu 26.7 m a ocupat locul 3. Pimii 2 au cistigat din partea lui Thomas cite un fir Zimsen cu head de 22 si 16 m. Masurarea distantelor de lansare a fost facuta de instructori.
Sectiunea pentru instructori a fost haioasa, caci s-a folosit o lanseta Zimsen de clasa 5 cu firul Zimsen de casting cu head de 22 m, chiar daca se putea folosi orice lanseta pe care o aveau, astfel dupa seria de lansari facute de ei, Thomas fiind ultimul, a venit cu lanseta de 18 picioare, just for fun, si dupa momentul in care s-au spulberat toate “pariurile” a lansat cu aceeasi lanseta ca toata lumea. Clasamentul final a fost Sasa cu 33.8m, Paul Arden cu 33.4m, Lasse cu 32.7m, Thomas cu 31m, Paul Sas cu 27.3m si Djordje cu 26.8m. Regulamentul a fost identic cu cel al participantilor.
Dupa asta s-a trecut la echipamentul greu, lanseta de 18 picioare cu care s-a aruncat peste gard si pomi, lansarile fiind peste 45 m.

Dupa prinz a venit si momentul final, al ceremoniei de inchidere. Astefel in curtea pensiunii s-au acordat dimplome participantilor, cele 2 fire puse la dispozitie de Thomas pentru cei 2 cistigatori ai concursului de casting, si am acordat instructorilor titluri alaturi de un vin Carama Ferdi de editie limitata. Astfel Paul Sas si Lasse au devenit membri de onoare a clubului nostru, Sasa si Thomas au devenit Muscarici Seniori ai clubului, iar Paul Arden si Djordje au devenit Instructori asociati. Am multumit pentru prezenta celor din Chisinau, gazdelor pentru ospitalitate si ne-am luat ramas bun, curtea arhiplina cu masin si lume raminind goala.
Titus cu Sasa s-au intors in Timisoara, Paul Sas a plecat spre Cluj.

Am pornit pe vale in sus cu Paul, Lasse, Thomas la pescuit, Paul cu Alex Varga s-au du pe coada lacului Gura Vaii sa vada daca merge ceva, noi ( Lasse, Thomas si eu) am ramas in zona primului pod pe Lapusnicul mare pentru avedea daca se ridica ceva la musca uscata. Nu a fost o zi buna, caci apa e inca foarte rece, si pastravii nu se ridica. Nu am incercat la nimfa, caci scopul nostru nu a fost sa scoate cu orice pret pesti din apa, ci am vrut mai mult sa vada apele si zona de pescuit.
Seara ne-am intors la pensiune pentru o cina linistita, si dupa citeva beri Caster si vin Ferdi ne-am dus la culcare.

Luni 29 iunie, am pornit la pescuit in zone noi. Paaul Arden s-a dus pe lac la revarsarea riului Ses, noi am plecat pe riul Brabat sa-l vada. Am ajuns in prima parte a riului dupa intrarea pe vale si am incercat un pic sa pescuim sa vedem daca sint ridicari la uscata. Djordje si eu am incercat la nimfa, in ideea de a vedea cum se comporta lansete Evil Fly, Djordje cu ce de clasa 3, eu cu cea de clasa 2. Dupa o plimabre in sus pe riu si mici incercari, am hotarit sa mergem in zona barajelor in aval sa incercam acolo, si apoi mai jos la iesirea de pe vale. S-au prins citiva pastravi frumusei, dar toti numai la nimfa, nu muscareau inca.
Pentru a face o zi cit mai completa, ne-am intors pe riul mare sa pescuim seara la uscata, sa vedem daca se ridica pastrvi mai frumosi. Am avut un drill cu un pastrav mai mare la uscata, apoi Thomas a avut ridicari de la pastravi mai mici, iar Lasse si Djordje ne-au ajuns din urma la un loc foarte bun, unde ne-am jucat cu fire si lanste diferite in casting la uscata upstream si downstream. A fost super fain, buna dispozitie, analiza de locuri si situatii, incercat de echipament, de toate.
Ne-a prins seara usor si am plecat spre pensiune pentru o cina buna si o degustare de vinuri Ferdi, lasate de Fernando Mihailescu in acest scop.

Marti 30 iunie, de dimineata ne-am imbarcat in masini si am pornit spre Timisoara, era ziua plecarii la aeroport a lui Lasse si Thomas, Djordje si Paul deasemenea porneau si ei spre casa. Pe la ora 12 am ajuns in oars si am hotarit ca mergem undeva spre aeroport pentru un ultim prinz in aceasta formatie. Ne-am oprit la Taverna Sirbului si dupa asta ne-am dus cu totii la aeroport. Pe Paul l-am condus la iesire din oras spre Cenad, iat Titus l-a condus pe Djordje spre Beograd. MCD8 se incheiase, noi am mers la birou pentru urgentele ce au aparut intre timp, si seara spre casa.
Sentimentul care s-a asternut a fost de mutumire pentru tot ce s-a intimplat, zile frumoase petrecute cu oameni minunati. Feedback-urile au inceput sa apara o data cu vestile de ajungere acasa cu bine a tuturor.
Sint zile ca au meritat sa fie traite!

Desigur ca multumirile noastre se indreapta spre participanti, instructori, si cei care ne-au sprijinit in acest proiect: Heinrich Loth – Data Group INT si Clinica de Bere, autorul berii Caster Intensive, pusa cu generozitate la dispozitie si finantare, Adrian Savu – Alsa Skog Norvegia pentru finantare, Alin Neamtu – BN Business pentru birotica necesara evenimentului, Fernando Mihailescu – Crama Ferdi, pentru vinurile exceptionale puse la dispozitie, Florin Doru Moza – Mopeka Impex, carburant, Florin Ivanescu pentru trofeele create pentru instructori, Titus Nicoara –  Ceradez, pentru suport si finantare. 


Muscarici Fly Casting Day editia a 8-a a avut loc de vineri 26 iunie ora 15.00 pina duminica 28 iunie 2015 ora 14.00, la Pensiunea Dumbravita de pe Riul Mare Retezat, Masivul Retezat.

Este un eveniment dedicat Fly Casting-ului, si echipamentului dedicat, eveniment ce va avea 3 sectiuni: – incepatori si copii (Beg) – avansati – casting echipament pentru o mina (SH) – casting cu echipament pentru 2 miini (DH)

Invitati:
Lasse Karlsson, MCCI THCI IFFF, CBOG AAPGAI, KarlssonFlyfishing.com (DK)
Paul Arden, Sexyloops (UK)
Thomas Berggren, IFFF MCI THCI, KarpenFlyFishing (SE)
Djordje Andjelkovic, IFFF MCI, THCI (SRB)
Sasa Zec, EFFA CI (SRB)
Paul Sas EFFA CI (RO)

Demonstratii, workshopuri, casting clinic, concurs de casting, prezentari de echipament si conferinte despre dezvoltarea de echipament de fly.
Este un eveniment deschis tuturor celor interesati.

De mentionat:
1. In pemiera – 6 instructori de casting acreditati prezenti in Romania din care 4 sint Master atit pentru echipament de o mina cit si pentru doua miini, campioni mondiali de casting, din UK, Danemarca, Suedia, Serbia si Romania.
2. In premiera – prezenta primului instructor Roman acreditat EFFA ( European Fly Fishing Association ) Paul Sas din Cluj.
3. In premiera – primul membru CBOG IFFF prezent in Romania, Lasse Karlsson din Danemarca, membru in Board of Governors, International Federation of Fly Fishers.
4. In premiera – O sesiune de casting nocturn cu fire speciale luminiscente marca Sexyloops, coordonata de Paul Arden (fondator Sexyloops.com – cel mai important portal de informatii si tehnica de casting).
5. 5 demostratii de casting de o ora sustinute de instructorii invitati, 12 workshopuri de cite 2 ore si jumatate sustinute in paralel pe sectiuni ( incepatori, avansati, si echipament pentru 2 miini ), 3 conferinte despre creare si dezvoltare de echipament, discutii despre programele IFFF.
6. 2 lansari de branduri in Romania: Zimsen din Suedia si Evil Fly din Serbia, lansete si fire.
7. 6 branduri prezente in eveniment: ECHO (USA), Loop (Suedia), Barrio (UK), Sexyloops (UK), Karpen FlyFishing (Suedia) si S1waterbike (Romania)
8. 45 de participanti din Romania, Germania, Republica Moldova.
9. Evenimentul contine citeva intilniri de notabile:
– discutii de lucru in cadrul FRPMA intre membrii cluburilor prezente la eveniment,
– Intilnire de lucru a Clubului Muscaricilor din Timisoara cu Fly Fishing Romania in privinta proiectului de renaturare a riului Ses.
10. Lansarea noului tip de bere al Clubului Muscaricilor din Timisoara: Caster Intensiv, bere produsa exclusiv pentru acest eveniment de Clinica de Bere din Timisoara.
11. Prezentarea si promovarea bogatiilor culturale si naturale ale zonei tarii Hategului.

3 zile intense, ce aduc Romania pe harta casting-ului international, evenimentul este considerat de instuctori ca fiind unul dintre cele mai importante din Europa de Est, in acest an.

Acest eveniment face parte din calendarul de activitati al FRPMA.

MCD8 Program:
Vineri 26 iunie:
pina la 3 PM – registration 3 PM – inceperea evenimentului, prezentarea instructorilor
4 PM – primul Demo – Lasse Karlsson – A mythbusting, taking apart several of the persistent myths in flycasting!
5 PM – Workshop: – BG (Paul Sas, Sasa Zec) – SH (Paul Arden, Lasse Karlsson) – DH (Thomas Berggren, Djordje Andjelkovic)
7.30 PM – cina
8.30 PM – Conferinta, Thomas Berggren – Zimsen lansare brand
9.30 PM – Conferinta, Lasse karlsson – ECHO prezentare echipament 10 PM – Lansare bere Caster Intensive, Lasse si Thomas despre programele IFFF

Sambata 27 iunie:
9 AM – mic dejun
10 AM – al doilea Demo – Thomas Berggren – Rod action and Line profiles – Does it really matter??
11 AM – Workshop: – BG (Paul Sas, Sasa Zec) – SH (Paul Arden, Thomas Berggren) – DH (Lasse Karlsson, Djordje Andjelkovic)
1.30 PM – al treilea Demo – Sasa Zec – Trick casts & Water Casts.
2.30 PM – prinz
3.30 PM – al patrulea Demo – Paul Arden – Developing the core skills.
4.30 PM – Workshop: – BG (Paul Sas, Djordje Andjelkovic) – SH (Paul Arden, Sasa Zec) – DH (Thomas Berggren, Lasse Karlsson)
7 PM – cina
8 PM – Conferinta, Djordje Andjelkovic – EvilFly lansare brand, Barrio noutati
9 PM – Paul Arden, Sexyloops Lumiline Demo – Sarmizegetusa Roman Forum, si degustare de vinuri Ferdi.

Duminica 28 iunie:
9 AM – mic dejun
9.45 AM – Demo 5 – Djordje Andjelkovic – Casting big and heavy flies
10.45 AM – Workshop: – BG (Paul Sas, Sasa Zec) – SH (Paul Arden, Lasse Karlsson) – DH (Thomas Berggren, Djordje Andjelkovic) 
1 PM – Competitie de Casting
2 PM – prinz
3 PM – Ceremonie de inchidere

Date tehnice: – echipament prezent in eveniment:
Evil Fly Rods ( lansare ) – brand al lui Djordje Andjelkovic: Nymph Whisperer 10 ft size 2,3,4, Nymphomaniac 11 ft size 3 and 12 ft size 4.
Zimsen ( lansare ) – seria de lansete de clasa 5 de 9 feet Medium, Medium Fast, Fast, lanseta de clasa 6 de 9 feet Fast1 si seria de fire tehnice Zimsen de clasa 5: MPL9, MXP12, MXD LB16, si MXD LB22.
Barrio, prin Djordje Andjelkovic line developer, va fi prezent cu firele sale GT 125, SLX si Nymph Line. Djordje le va prezenta in conferinta sa.
Sexyloops, Karpen FlyFishing, Loop, Echo, S1waterbike.

Partener oficial al clubului: Clinica de Bere – Timisoara, care produce berea Caster pentru acest eveniment, sa lansat cu aceasta ocazie noua bere Caster Intensiv.

Parteneri: Crama Ferdi, Alsa Skog, BN Business, Mopeka Impex, Data Group Int, Ceradez, Ideatm, MMC.
MCD8a505

Muscarici Fly Casting Days – edition 8, is part of a series of Fly Casting events held with certified casting instructors in Romania since 2010.
The edition 8 took place in Retezat Mountains, western part of Romania – at Dumbravita Pension on June 26- 28, 2015.

The event was open to every fly fisherman, beginner or advanced caster, for one hand or double hand gear.

Invited instructors and guests are:
Lasse Karlsson MCCI THCI IFFF, CBOG AAPGAI (DK)
Paul Arden – Sexyloops founder (UK)
Thomas Berggren MCI THCI IFFF (SE)
Djordje Andjelkovic MCI THCI IFFF (SRB)
Sasa Zec CI EFFA (SRB)
Paul Sas CI EFFA (RO)

3 days dedicated to casting techniques: Demos, Workshops, Casting clinic, Gear presentation and gear tests, Conferences about developing gear.
3 working sections: 1.- One hand (SH), 2. – Two hands (DH), 3. – Beginners and casting for kids.

You could find:
– Designing and developing gear conferences,
– Gear show and test,
– Casting Competition,
– Fishing Demos on stream and lake,
– International participation,
– Caster Intensive beer launch – Muscaricilor Club new beer .

The event was part of Romanian Fly Fishing Federation (FRPMA) calendar.

Event language: English

Brands in the event:
Sexyloops, Zimsen, Karpen FlyFishing, Loop, ECHO, Evil Fly, Barrio, S1waterbike.

Official Partner of Clubul Muscaricilor Timisoara: Clinica de Bere – the Caster Platin and Gold beer producer.

MCD8 Program:
Friday June 26:
till 3PM – registration 3 PM – starting the event registration presenting the instructors
4 PM – First Demo – Lasse Karlsson’s hour – A mythbusting, taking apart several of the persistent myths in flycasting!
5 PM – Workshop – BG (Paul Sas, Sasa Zec) SH (Paul Arden, Lasse Karlsson) DH (Thomas Berggren, Djordje Andjelkovic)
7.30 PM – diner
8.30 PM – Conference, Thomas Berggren – Zimsen brand launch
9.30 PM – Conference, Lasse karlsson – ECHO gear presentation 
Caster Intensive beer launch, Lasse and Thomas about IFFF programs

Saturday June 27:
9 AM – breakfast
10 AM – Second Demo – Thomas Berggren’s hour – Rod action and Line profiles – Does it really matter??
11 AM – Workshop – BG (Paul Sas, Sasa Zec) SH (Paul Arden, Thomas Berggren) DH (Lasse Karlsson, Djordje Andjelkovic)
1.30 PM – Third Demo – Sasa Zec’s hour – Trick casts & Water Casts.
2.30 PM – lunch
3.30 PM – Fourth Demo – Paul Arden’s hour – Developing the core skills.
4.30 PM – Workshop – BG (Paul Sas, Djordje Andjelkovic) SH (Paul Arden, Sasa Zec) DH (Thomas Berggren, Lasse Karlsson)
7 PM – diner
8 PM – Conference, Djordje Andjelkovic – EvilFly brand launch
9 PM – Paul Arden, Sexyloops Lumiline demo – Sarmizegetusa Roman Forum, Ferdi vines

Sunday June 28:
9 AM – breakfast
9.45 AM – Fifth Demo – Djordje Andjelkovic’s hour – Casting big and heavy flies.
10.45 AM – Workshop – BG (Paul Sas, Sasa Zec) SH (Paul Arden, Lasse Karlsson) DH (Thomas Berggren, Djordje Andjelkovic)
1 PM – Casting Competition
2 PM – lunch
3 PM – Closing ceremony, certificates, good bye

To notice:
1. Premiere – 6 accredited casting instructors at one event in Romania, 4 MCI and THCI, from UK, Denmark, Sweden, Serbia si Romania.
2. Premiere – first Romanian accredited EFFA instructor Paul Sas from Cluj.
3. Premiere – first CBOG IFFF in Romania, Lasse Karlsson from Danemarca, member in Board of Governors, International Federation of Fly Fishers.
4. Premiere – a night casting session with Luminous line from Sexyloops, coordinated by Paul Arden (Sexyloops).
5. 5 one hour casting demos, 12 workshops 2hours and a half each held in 3 sections ( beginners, single hand and double hand), 3 conferences about designing and developing gear and IFFF programs.
6. 2 brand launch in Romania: Zimsen from Sweden & Evil Fly from Serbia, rods and lines.
7. 6 brands in the event: ECHO (USA), Loop (Sweden), Barrio (UK), Sexyloops (UK), Karpen FlyFishing si S1waterbike (Romania)
8. 45 participants from Romania, Germany, Republic of Moldavia.
9. 2 Important meeting:
– working session in Romanian Fly Fishing Federation,
– working meeting between Clubului Muscaricilor from Timisoara and Fly Fishing Romania concerning the rehabilitation project of Riul Ses, Retezat.
10. Clubului Muscaricilor from Timisoara new beer launch: Caster Intensiv, exclusively produced by Clinica de Bere din Timisoara for our club event.

3 intense days, that bring Romania on the international casting map, the event is considered by instructors as a top event.

The Story:

The event starts on Thursday June 25, with the arrival of Thomas and Lasse to Timisoara International Airport. I went to pick them up and drive to Castel Royal Timisoara to meet Dordje and Paul Arden at a nice meal. It was 6 PM when we met all there and we start drive to the Retezat Mountains to get there before dark. We had a small stop to Sarmizegetusa Roman Arena and Forum, to see if it is OK for the Luminous Line session programed to Saturday evening. The Forum was OK, but beacuse of the ambient light of the village the arena wasn’t a place for the session.
We arrived a Dumbravita Pension, and we meat the guys from Flyfishing Romania, Smaranda and Liviu Neagoe, to talk about the days to come, and the partnership on Riul Ses project. We had many Caster beers late night.

Friday, June 26, morning we meat the muscarici guys from Deva, they come to help us on arranging the banners and preparing the event starts. We drive to the upper valley to show to Paul, Thomas, Lasse and Djordje the area for fishing. So we went to the Gura Apei dam and up to the Lapusnicul Mare stream. We had a wonderful journey, and we went back to the pension for noon. There a lot of people where arrived, we meat Paul Sas and Sasa, and we prepare to start the event.
At 4 PM, I presented the invited instructors and Lasse start with his one hour demo – a myth busting of the most common casting tabus. A great demo, talking about anchor, more weight get distance, rod action, fast versus medium, etc.After this demo, we split into sections and we start the workshop first row. Being on DH section, I went with Djordje and Thomas to the Ostrov lake to meet the others and start the topic we had to do. Lift off, Swich cast, was the focus.
We had a continuous rain on the lake, so after 2 hours and a half, we leave to the pension for diner.
The evening start with Thomas conference about Zimsen rods and lines, a very nice presentation focus on rod action and lines profile, with the focus on learning more about general aspects on developing, and choosing a rod action. Great conference.

Later Lasse presented the Echo gear, focus on the Boost new series and Glass series. it was interesting to understand the choice of Tim Rajef on the old fiber glass action, and we could hear the Echo gear grounds.
With plenty of Caster beer the night was long, and people talk about all sorts of things till morning.

Saturday, June 27
Morning came with Thomas hour demo, continuing what he start a evening ago, presenting the rod action matter. than we did some work on the grass on the back side lawn of the pension, trying the rods and lines. Than Sasa demo about trick cast and water casts that started on the lawn and after lunch, continued on the Ostrov lake shore. Than Paul Arden start his demo about developing core skills, a very nice demo about the way of developing the classic casts in your own way. We spend the rest of the day on the lake shore to develop the skills in Double Spey, avoid the “Bloody L” on the DH section.
The evening came so before we went to diner, I took Thomas and Lasse up on the fromt hill to see the magnificent view above Hateg County and Retezat Mountains. It was a short but nice time to see clouds and rain moving above our heads.
After diner we had a short Romanian FFF meeting, and than Djordje presented the Barrio lines and his Evil Fly Nymphing rods. Later Lasee Thomas and Paul Arden talk about the Casting World Competitions, stories about participants, and what it should be done for a Romanian team in future.
In the mean time we start to prepare the casting night session, testing the charger for Lumilines, and off-course in the late moment shit happen and we had to fix the charger contacts. People gathered on the lawn and we manage to charge 3 line to have people cast with late in the night. It was a very nice moment, seeing all those luminescent lines flowing into the air. Great lines and moment.

Sunday, June 28
We start in the morning with Djordje’s demo about casting big and heavy flies. A nice demo using big… flies, and trying to cast them far, different techniques on heavy rods. Later we went to lake shore to have the final workshops on DH rods, the SH and beginners worked on the pension lawn. We did snake roll cast in DH, and we tried the Thomas 18 foot competition rod with a 27 m head… hard to have a lift off wit that gear.

At noon we came to the pension to arrange the competition place, we decide that we shall do only the distance competition because of the lack of time, and we had a special task on doing as far and many casts in only one minute. We had 10 participants, and the instructors supported us in measuring each cast. In the end we had Alex Moga on first place with 28.3m, Luca Moga on second place with 27.2m and Titus Nicoara on third place with 26.7m. The instructors made their own section, so after a funny moment in which Thomas bring his 18 footer rod, we had the final results with all on the same rod ( Zimsen) Sasa first place with 33.8m, Paul Arden on second with 33.4m and Lasse on third with 32.7m. It was fun, the average rate of cast was 4 in one minute.

After lunch we star tour closing ceremony, thanks to all participants for being here with us in this event, thanks to instructors for teaching and give them honorific titles of our club, so Paul Sas and Lasse get the honorary membership of our club, Paul Arden and Djordje became Associate Instructors, and Sasa and Thomas became our Senior Members.
We thank to Jarco, our host for all his support and to all partners and sponsors.

People went homes, and Paul Arden, Lasse, Thomas, Djordje and I went to the upper part of the valley for fishing into Lapusnicul mare stream and Gura Apei lake. We had a nice afternoon there and we tried to have a dry fly fishing in a very cold water. No fish, but it is normal to the water condition. So we went in the evening to have a nice meal and plan the next day for fishing.

Monday, June 29
We start the day organizing fishing on Barbat river, and we start driving into the area. The landscapes are nice and we arrived at a first third of the valley to start fishing. Thomas and Lasse at dry fly, Djordje and I nymphing, I wanted to try the Evil Fly weight 2 rod. So after catching few trouts we decided to go downstream to see the dams part, and than in the entrance of the valley. We had some trouts there too, and we decided to see the evening fishing on Riul Mare. So we went to the lower part of the river and we did some Dry Fly Fishing there, catching some trouts and seeing some nice places to fish. Evening came quickly and we went to meet Paul Arden at the pension, cause he went all day in the Gura Apei lake on the Riul Ses part. He had some experience climbing to the car on a very long and steep shore. Wild and rough places. We had a nice meal and Ferdi wines late into the night.

Tuesday, June 30
Th departure day, we had to get up early and pack the cars, starting to drive to Timisoara for geting in time to the airport, Thomas and Lasse has to fly home, Paul Arden and Djordje has to drive home. So after a lunch near the airport, we pass Thomas and Lasse to check in, than we went to the exist of the town with Paul and Djordje. The MCD8 was over.
Time to write emails, press releases, grabbing all photos we made, publish interviews, etc… and still today I’m not ready with all that.
But as I like to say, those days are worth to be living!

Technical data: – gear:
Evil Fly Rods ( launch ) – Djordje Andjelkovic brand consist in nymphing rods: Nymph Whisperer 10 ft size 2,3,4, Nymphomaniac 11 ft size 3 and 12 ft size 4.
Zimsen ( launch ) – rods weight 5, 9 feet Medium, Medium Fast, Fast, weight 6, 9 feet Fast1 and technical lines Zimsen weight 5: MPL9, MXP12, MXD LB16, si MXD LB22.
Barrio, through Djordje Andjelkovic line developer, presented the GT 125, SLX si Nymph Line.
Sexyloops, Karpen FlyFishing, Loop, Echo, S1waterbike.

Oficial Partner: Clinica de Bere – Timisoara, the producer of Caster beer for this event, we had Caster Intensiv launch beer.
Partners: Crama Ferdi, Alsa Skog, BN Business, Mopeka Impex, Data Group Int, Ceradez, Ideatm, MMC.